Security as Code - A DevSecOps Approach
Explore DevSecOps and Security as Code with CodeQL. Learn to implement security checks, detect vulnerabilities, and foster collaboration between development and security teams for a robust security culture.
Secure Your Project with the SIG Release Supply Chain Kit
Explore tools for enhancing supply chain security in open-source projects, including SBOMs, signed attestations, and secure release pages. Learn how to implement these features using reusable GitHub actions.
In-Toto: Attestations and Software Supply Chain Security
Explore in-toto framework's advancements in software supply chain security, including attestation verification, type mapping, and integrations with CNCF projects and industry tools.
Putting the Supply Chain Pieces Together: A Deep Dive into the Secure Software Factory
Explore a deep dive into supply chain security, focusing on implementing CNCF's Secure Software Factory architecture using cloud-native tools to enhance software provenance and artifact trustworthiness.
Securing the Supply Chain with Witness - A Framework for Supply Chain Security
Explore Witness, an open-source framework for supply chain security, its trust model, and implementation in CI pipelines. Learn about attestation collections, policy enforcement, and integration with cloud-native tools.
Securing Your Container Native Supply Chain with SLSA, GitHub and Tekton
Practical guide to securing container native supply chains using SLSA principles, in-toto attestations, and step-by-step demos for achieving SLSA Level 2 in Tekton and Github Actions.
Secure Containers and Workloads with Certificates in CI/CD Pipelines
Learn to enhance security in CI/CD pipelines by implementing certificate-based protection for containers and workloads, ensuring robust safeguards for cloud-native applications.
Growing the Chain: Trusting Build Provenance from Userspace
Explore techniques for establishing trust in CI/CD workflows, focusing on artifact signing, provenance generation, and building a chain of trust using open-source technologies like Sigstore and OIDC.
How to Generate VEX Automatically for Your Project
Learn to automate VEX generation for Kubernetes workloads, reducing false positives in security scans and streamlining vulnerability management using Kubescape and a new GitHub Action.

Securing the Supply Chain: A Practical Guide to SLSA Compliance from Build to Runtime
Practical guide to securing software supply chain using CNCF tools. Covers SLSA compliance, GitHub Actions, Cosign, Kyverno, in-toto, and Kubescape for build-to-runtime security in Kubernetes ecosystems.
DevSecOps Transformation at Speed and Scale Using Tekton
Standardize CI/CD security automation, centralize platform operations, and prevent software vulnerabilities using Tekton as an open-source orchestrator with integrated scanning tools and continuous compliance.
Under the Radar: How We Found 0-Days in the Build Pipeline of OSS Packages
Explore critical vulnerabilities in OSS build pipelines, including 0-day discoveries in major projects. Learn about attack trees, mitigations, and 'Living Off the Pipeline' components for enhanced security.
Implementing DevSecOps in Production with Stackrox and Tekton
Implement robust DevSecOps pipelines using Stackrox and Tekton. Eliminate security risks, secure the software supply chain, and provide automated guardrails for developers.
Keep it Clean: QA Automation with Linters from Yocto - 2023/11/28
Explore QA automation tools for debugging shellscripts, systemd, bitbake recipes, and packaging issues in Yocto Project builds, with seamless CI integration.
Building a Yocto CI Pipeline with KAS, GHActions and AWS
Explore building a Yocto CI pipeline using KAS, GitHub Actions, and AWS for efficient embedded systems development and deployment.
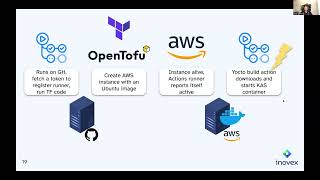
Building a Yocto CI Pipeline with KAS, GitHub Actions, and AWS - YPS 2023.11
Explore CI pipeline creation for Yocto using KAS, GitHub Actions, and AWS. Learn to overcome challenges and implement effective strategies.
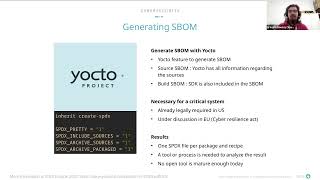
The LF Energy Seapath Project: Yocto Applications in Power Grid Automation
Explore SEAPATH, an open-source platform for power grid substation automation. Learn about its development, transition to virtualization, and the role of Yocto in cybersecurity, SBOM, CI/CD, and licensing.
Automating Yocto Layer Maintenance with Cloud Managed Services - Thomas Roos
Automate Yocto layer maintenance using cloud services to save time, upgrade software, test recipes, and backport changes efficiently.
Let Devs Be Devs Without Sacrificing Security
Explore flexible, secure CI pipelines using Tekton, Chains, and Enterprise Contract to balance developer innovation with robust security measures for various software targets.
Enforcing Organization Policies with Enterprise Contract
Learn to enforce organizational policies on container images using Enterprise Contract, leveraging Sigstore signatures and in-toto attestations within the Tekton ecosystem.
Codifying Privacy: How to Follow Through On Your Privacy Promises
Learn practical approaches to implement privacy promises in software development, focusing on embedding privacy in CI/CD pipelines and overcoming common hurdles to ensure data handling aligns with user-facing policies.