Revolutionizing Software Development with Feature Flags and Chaos Engineering
Explore feature flags for enhanced software reliability, agile response, and business impact. Learn integration with chaos engineering for improved development practices.

Avoiding Static Shared Secrets in GitHub Actions
Learn best practices for securing GitHub Actions workflows, avoiding static shared secrets, and implementing safer alternatives for CI/CD pipelines.
Setting Up and Managing GitHub Actions for Multiple Projects
Learn to set up and manage GitHub Actions across multiple projects efficiently, with insights on starter actions, organization reports, and custom workflows for Java and Python repositories.
CI/CD - Build and Deploy Automation
Explore CI/CD build and deploy automation techniques for efficient cloud-native development and streamlined software delivery pipelines.
The New Wave of Deserialization Bugs
Explore deserialization vulnerabilities in Java, PHP, and Python. Learn to identify and mitigate risks in enterprise applications using practical examples and tools.
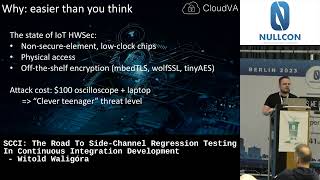
The Road to Side-Channel Regression Testing in CI Development
Explore integrating side-channel regression testing into CI development, with practical demonstrations and insights on implementing countermeasures for sample attacks.
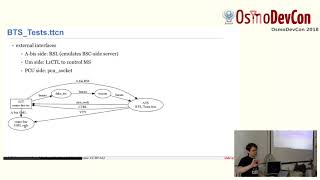
State of the Osmocom TTCN-3 Test Suites
Comprehensive overview of Osmocom TTCN-3 test suites, covering their status, testing methods, and automation using Jenkins and Docker for mobile network protocols.
Security DevOps - Staying Secure in Agile Projects
Explore security integration in agile projects through dynamic depth, static depth, intensity, and consolidation axes. Learn practical DevOps techniques for maintaining security throughout development.
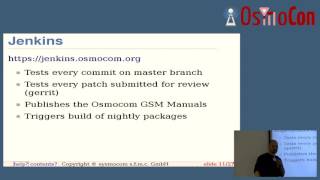
Osmocom Project Infrastructure - Redmine, Mailman, Git, Gerrit, Jenkins
Explore Osmocom's open-source infrastructure: communication tools, project management, version control, and continuous integration for efficient FOSS development.
A Practical Guide to Fuzz Testing Embedded Software in a CI Pipeline - Dennis Kengo Oka - Ekoparty 2021: Hardware Hacking Space
Practical guide to implementing automated fuzz testing in CI pipelines for embedded software, using Zephyr RTOS as an example. Learn strategies, execution, and vulnerability detection.
Interact Differently - Get More from Your Tools Through Exposed APIs
Explore how to leverage exposed APIs and plugin interfaces in software tools to enhance functionality, streamline workflows, and create custom solutions for improved efficiency and effectiveness.
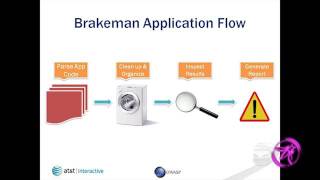
Brakeman & Jenkins - The Duo Detects Defects in Ruby on Rails Code
Explore static analysis tools for Ruby on Rails, focusing on Brakeman and Jenkins integration. Learn about security warnings, code updates, and best practices for detecting defects.
AppSec Pipelines and Event-based Security - Moving Beyond a Traditional Security Test
Strategies for scaling AppSec programs using automation, continuous health checks, and event-based security to keep pace with rapid software development and delivery in large organizations.
Open Source Security Tools for Kubernetes Applications
Explore open-source tools for securing Kubernetes applications, covering image scanning, runtime security, and anomaly detection. Learn practical strategies for maintaining a secure cloud-native environment.
Controlled Mayhem With Cloud Native Security Pipelines
Explore cloud-native security pipelines, comparing traditional and modern approaches, while addressing challenges in container orchestration, access control, and CI/CD processes.
Living on Master - Using Yocto Project, Jenkins and LAVA for a Rolling Release
Explore continuous integration for Yocto Project using Jenkins and LAVA, focusing on real-time Linux kernel testing and addressing challenges in maintaining up-to-date embedded systems.
Recipe for Modern Applications - .NET Azure SQL Functions Geospatial JSON
Discover how to build modern applications using Azure SQL, .NET, and Azure Functions. Learn about JSON, geospatial data, scalability, and CI/CD in a real-world scenario.
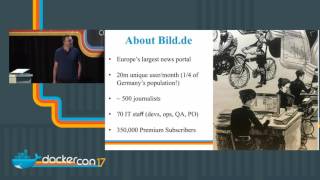
How a Large Media Company Uses Splunk for Analytics-Driven Container Performance and Logging
Discover how BILD GmbH leverages Splunk for container performance monitoring, logging, and troubleshooting in their news portal infrastructure, offering insights for developers and operations teams.

Building a Secure Docker Application
Learn to leverage Docker's security features, from content trust to network segregation, to build and deploy secure applications in a streamlined development pipeline.
Node.js Rocks in Docker for Dev and Ops
Optimize Node.js development and deployment in Docker with best practices for Dockerfiles, image building, process management, security, and performance enhancements for local and production environments.
Android Meets Docker
Explore Docker's impact on Android development, enhancing CI, ensuring consistent environments, and solving common issues. Learn setup, benefits, and limitations through examples and live demos.