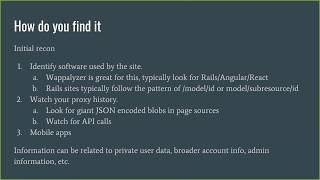
Hidden in Plain Site - Disclosing Information via Your APIs - Peter Yaworski, Bugcrowd's LevelUp 2017
Explore information disclosure vulnerabilities in APIs and HTML sources, focusing on Rails design patterns and front-end frameworks. Learn detection techniques and real-world examples.
Doing Recon Like a Boss - Ben Sadeghipour, Bugcrowd's LevelUp 2017
Learn efficient hacking reconnaissance techniques, including methodologies for Amazon AWS, GitHub, asset identification, and QA, to enhance your cybersecurity skills and target assessment capabilities.
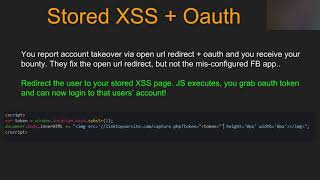
Giving Back to the Bug Bounty Community - ZSeano, Bugcrowd's LevelUp
Learn advanced bug bounty techniques from top hacker ZSeano. Discover web vulnerabilities, improve your skills, and gain insights on professional conduct in the cybersecurity field.
Breaking Mobile App Protection Mechanisms - Ben Actis, Bugcrowd's LevelUp
Learn to identify and bypass mobile app protections like obfuscation, root detection, and certificate pinning. Discover techniques to reduce "hardened" apps to basic security levels.
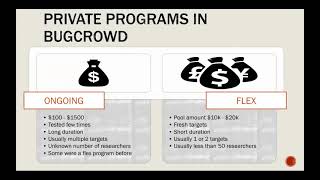
Finding Hidden Gems in Old Bug Bounty Programs - Yappare, Bugcrowd's LevelUp 2017
Discover strategies for uncovering valuable bugs in established bug bounty programs, focusing on unique approaches and methodologies to maximize success in competitive environments.
How to Fail at Bug Bounty Hunting - Caleb Kinney, Bugcrowd's LevelUp 2017
Insights and tips for part-time bug bounty hunters: overcoming challenges, learning from failures, and staying motivated while balancing professional commitments.
Bug Bounty Hunting Methodology - Jason Haddix from Bugcrowd's LevelUp
Comprehensive web hacking methodology covering reconnaissance, scanning, and exploitation techniques for bug bounty hunters and security researchers.
Esoteric Sub-Domain Enumeration Techniques
Explore advanced and unconventional sub-domain enumeration methods, their effectiveness, associated tools, and mitigation strategies for enhanced cybersecurity practices.
The State of Bug Bounties and Future Trends - Casey Ellis AMA
Insights on bug bounty industry trends, future prospects, and expert Q&A with Bugcrowd's CEO Casey Ellis, covering various aspects of cybersecurity and ethical hacking.
Writing Vulnerability Reports That Maximize Your Bounty Payouts
Learn to craft effective vulnerability reports that boost bounty payouts. Discover key strategies for communicating impact, providing proof of concept, and avoiding common mistakes in bug bounty submissions.
Pentesting vs Bug Bounty - Approaches and Methodologies
Explore the differences between bug bounty hunting and penetration testing methodologies, comparing approaches, impacts, and scoping techniques.
It's Not a Vulnerability, It's a Feature - Exploiting Built-in Functionality
Explore how offensive security has evolved from CVEs to TTPs, and learn to leverage built-in features for security testing and potential monetization through creating and sharing TTPs.
Car Hacking Explained for Bug Hunters - Automotive Security Vulnerabilities and Methodologies
Explore automotive security vulnerabilities, from IoT to CAN bus hacking. Learn methodologies, attack surfaces, and bug prioritization for car hacking, covering infotainment systems, APIs, and mobile apps.
Sticking With It: How to Choose a Target and Stay Motivated in Bug Bounty Programs
Learn strategies for selecting bug bounty targets, maintaining motivation during hacking, and deciding when to persist or move on. Gain insights from an experienced researcher on navigating the challenges of bug hunting.
Overview of Common Android App Vulnerabilities
Explore common Android app vulnerabilities, their detection, and remediation. Learn about Google Play's security programs and essential resources for developers to enhance app security.
Bug Bounty Recon Basics - Part 1
Learn essential bug bounty reconnaissance techniques, including subfinder, Google dorking, data manipulation, ASN analysis, Shodan basics, and more for effective vulnerability discovery.
Bug Bounty, DEFCON CTF, and Smart Contracts Discussion with ret2jazzy
Insightful discussion on bug bounty programs, DEFCON CTF experiences, and smart contract security, offering valuable perspectives for cybersecurity enthusiasts and professionals.
Read The Bleeping RFC - Understanding Network Protocols for Security
Explore RFC vulnerabilities and their impact on web security with Inti De Ceukelaire. Learn to identify and exploit logic flaws in protocols for more effective bug hunting and penetration testing.
Hacking, Content Creation, and API Security with TheXSSRat
Insightful discussion on hacking, content creation, and API security with TheXSSRat. Covers career paths, learning strategies, and practical tips for aspiring cybersecurity professionals.
Bug Bounty Methodology and Hacking the US Government - Interview with Jack Cable
Insights from a top bug bounty hunter on hacking methodology, government cybersecurity, and career advice for aspiring ethical hackers.
Advent of Cyber - Web Exploitation - Cross-Site Scripting (XSS) Explained
Comprehensive explanation of Cross-site Scripting (XSS) in web security, covering its types, risks, and prevention methods. Practical insights for ethical hackers and cybersecurity enthusiasts.