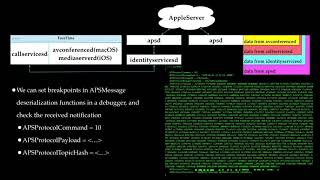
Towards Discovering Remote Code Execution Vulnerabilities in Apple FaceTime
Explore FaceTime's vulnerabilities through reverse engineering, focusing on call initialization, connection processes, and potential attack surfaces for remote code execution.
How the Best Hackers Learn Their Craft
Discover the proven system for building elite hacker teams, from talent identification to competition success. Learn surprising strategies for developing top-tier cybersecurity skills and fostering creative problem-solving abilities.
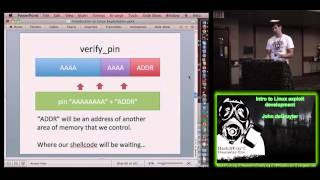
Intro to Linux Exploit Development
Explore Linux exploit development, covering buffer overflows, shellcode, and mitigation techniques. Hands-on labs and practical examples enhance understanding of system vulnerabilities and security concepts.
How to Hack Medical Imaging Applications via DICOM
Explore critical security vulnerabilities in DICOM servers, protocols, and libraries used in medical imaging systems. Learn to identify and fix bugs in the DICOM ecosystem.

Using Static Binary Analysis to Find Vulnerabilities and Backdoors in Firmware
Explore techniques for detecting vulnerabilities and backdoors in embedded device firmware using static binary analysis, focusing on challenges and automated solutions for complex binary blobs.
Advanced Windows NT - 2K Security
Explore advanced Windows NT/2K security, including payloads, buffer overflows, and kernel mode injection techniques for enhanced system protection.
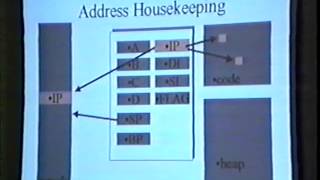
Advanced Buffer Overflow Techniques
Explore advanced buffer overflow techniques, including stack injection, heap exploitation, and protection bypassing. Learn about payload crafting, injection vectors, and dynamic function loading.
A Comparison of Buffer Overflow Prevention Implementations and Weaknesses
Comprehensive analysis of buffer overflow prevention techniques, exploring implementations and vulnerabilities to enhance cybersecurity strategies.
Deconstructing DeFeNeStRaTe.C
Dive into mainframe security with an analysis of DeFeNeStRaTe.C, exploring privilege escalation, APF unix programs, buffer overflows, and ACEE manipulation on IBM z/OS systems.
Software Security Era - Past, Present, and Future
Explore the evolution of memory corruption exploitation, from early techniques to modern mitigations. Includes live demos of vulnerabilities and discusses the ongoing challenges in software security.
Treble or Trouble - Where Android's Latest Security Enhancements Help And Where They Fail
Explore Android's security enhancements, focusing on Project Treble's impact. Analyze SELinux, Stagefright, and MediaDrmServer vulnerabilities to understand where improvements succeed or fall short.
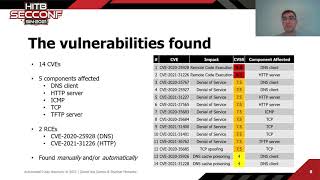
Squashing Low-hanging Fruit in Embedded Software
Discover advanced techniques for identifying and mitigating critical vulnerabilities in embedded systems, focusing on NicheStack TCP/IP stack vulnerabilities and automated vulnerability detection methods.
Contemporary Automatic Program Analysis
Explore automatic program analysis techniques for vulnerability discovery, from historical context to cutting-edge methods, with practical examples and demos for effective security research.
The Defense Rests - Automation and APIs for Improving Security
Explore automation and APIs for enhancing security through centralized management, testing, and evidence-driven approaches. Learn to leverage open-source tools and protocols for efficient vulnerability detection and faster recovery.
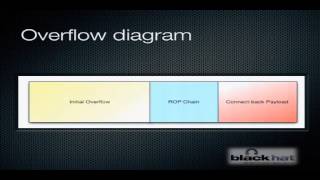
SQL Injection to MIPS Overflows - Rooting SOHO Routers
Explore SQL injection techniques to exploit buffer overflows and gain root access to Netgear routers, including file extraction and live demonstration of vulnerabilities in SOHO devices.
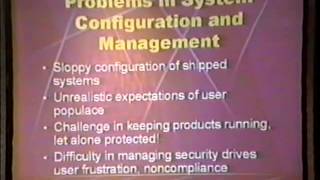
Computer Security - Textbook View
Explore computer security challenges, from software design to system management, with insights on trust issues, complexity, and evolving threats in the digital landscape.
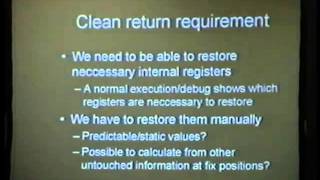
IDS Evasion Design Tricks for Buffer Overflow Exploits
Explore advanced buffer overflow exploit techniques and IDS evasion strategies, focusing on design tricks for more effective and stealthy attacks in network security.
So Hopelessly Broken - The Implications of Pervasive Vulnerabilities in SOHO Routers
Explore vulnerabilities in SOHO routers, covering security risks, testing methods, and exploit development. Learn about command injection, directory traversal, and buffer overflows with live demonstrations.
Moving Past Metasploit - Writing Your First Exploit
Learn to create custom exploits beyond Metasploit, focusing on buffer overflow techniques, Python scripting, and using Immunity debugger for more effective and reliable penetration testing.
Metasploit Fuzzing and Exploit Development
Learn advanced Metasploit techniques for fuzzing and exploit development, covering overflows, stack manipulation, and shellcode creation. Gain practical skills inspired by Derbycon's founding.
A Crash Course in Exploiting Buffer Overflows - Live Demos
Hands-on exploration of buffer overflow vulnerabilities with live demonstrations, providing practical insights into exploiting and mitigating these common security flaws.