BPF Observability Tools Update
Explore the latest advancements in BPF observability tools with expert Brendan G, gaining insights into enhanced system monitoring and performance analysis techniques.
Resurrection of /dev/bpf Discussion for Implementing Trusted Unprivileged BPF
Explore the revival of /dev/bpf for implementing trusted unprivileged BPF, delving into its implications and potential benefits for Linux kernel development and security.
Enabling Kfuncs to Specify Modifiers Per-Argument - Linux Kernel Development
Explore advanced BPF programming techniques, including kfunc modifiers, bpf_struct_ops operations, and local storage map types for enhanced kernel functionality.
Compiled BPF: Introduction and Fundamentals - Part 1
Explore the fundamentals of Compiled BPF with Jose E. Marchesi in this comprehensive introduction to the powerful Linux kernel technology.
Namespace-Unaware BPF Iterator and Cgroup Helper Enhancements for Kubernetes Environments
Explore BPF iterator enhancements for Kubernetes environments, focusing on namespace-unaware sockets and cgroup helpers to improve container networking and resource management.
Monitoring SRIOV with BPF
Explore advanced network monitoring techniques using BPF for SRIOV environments, enhancing performance and visibility in virtualized infrastructures.
Generic BPF Multi-Attach API and Implementation for TCX and XDP Meta Netdevices
Explore the new BPF multi-attach API and its implementation for tcx and XDP meta netdevices, enhancing network programming flexibility and performance.
BPF Documentation and Standardization Progress
Explore the latest advancements in BPF documentation and standardization efforts with insights from industry expert Dave Thaler.
FUSE BPF - Introduction to Filesystem in Userspace with Berkeley Packet Filter
Explore FUSE BPF with Daniel Rosenberg, learning about its applications and benefits in Linux systems for enhanced file system functionality and performance optimization.
BPF Iterator for File Systems
Explore BPF iterators for file systems, enhancing kernel observability and performance analysis in Linux environments.
BPF Signing Using FSVerity and LSM Gatekeeper
Explore BPF signing techniques using fsverity and LSM gatekeeper to enhance system security and integrity verification in Linux environments.
BPF Documentation and Standardization
Explore BPF documentation and standardization efforts, gaining insights into current practices and future directions for this powerful Linux kernel technology.
BPF Tales: Recompiling the Kernel to Average Numbers in Datacenters
Explore BPF for efficient data processing in datacenters, focusing on averaging numbers and optimizing storage operations through kernel-level programming.
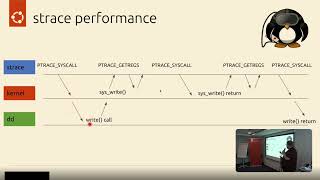
Bpftrace Recipes - 5 Real Problems Solved
Explore dynamic runtime tracing with bpftrace to solve real-world operational issues. Learn to write efficient kernel programs for analyzing and debugging complex system problems without modifying software or impacting performance.
Callsite Trampolines for Memory Allocation Profiling
Exploring compiler support for instrumenting call sites to store additional data, focusing on memory allocation profiling and its implications for Linux kernel development.
BPF_LSM and fsverity for Binary Authorization
Flexible binary authorization solution using BPF_LSM and fsverity for enhanced system security. Combines file integrity checksums, secure signing, and access control enforcement.
BPF for Security and LSM Updates
Explore BPF LSM advancements, including static calls, xattr operations, and security applications. Learn about challenges and future developments in kernel-level security.
BPF Programmable Netdevice - Introduction to Netkit
Explore BPF networking advancements, including tcx fast path and the new "netkit" programmable netdevice. Learn about its integration with Cilium and its potential impact on network infrastructure.
BPF-Based Packet Filtering Framework: bpfilter - Current Capabilities and Development
Explore bpfilter's evolution into a userspace daemon for dynamic packet-filtering BPF programs. Learn about its capabilities, performance, and ongoing development efforts.
Function Return Hook Integration with Function Graph Tracer
Explore integrating function return hook mechanisms to improve efficiency in Linux kernel tracing, addressing challenges of concurrent usage and memory allocation.
Function Parameters with BTF - Enhancing Function Tracing
Explore function tracing enhancements using BTF to display return values and arguments, improving debugging capabilities in Linux kernel development.