Intrusion Detection with Wazuh - Blue Team Series with Hackersploit
Comprehensive guide to Wazuh for intrusion detection, covering setup, configuration, and key features like agent management, integrity monitoring, and vulnerability assessment for enhanced cybersecurity.
HackerSploit Blue Team Series - Network Traffic Analysis with Wireshark
Comprehensive introduction to network traffic analysis using Wireshark for blue team operations. Covers Wireshark interface, filters, packet analysis, and practical exercises for security analysts and SOC teams.
Blue Team Hacking - Intrusion Detection with Snort
Learn to implement Snort, a leading open-source intrusion detection system. Covers installation, configuration, rule creation, and practical usage for effective network security monitoring.
Incident Response with Fireeye - Final Hackersploit Blue Team Training
Learn to use FireEye's Redline for incident response, including memory and file analysis. Gain practical skills in data collection, comprehensive collection, and analysis sessions for effective threat assessment.
Splunk Security Event Monitoring - Blue Team Series with Hackersploit
Learn to set up and use Splunk for security event monitoring, including installation, configuration, log forwarding, data analysis, and dashboard customization in this comprehensive tutorial.
Intrusion Detection with Suricata - Blue Team Series with Hackersploit
Learn to install, configure, and use Suricata for intrusion detection. Covers IDS, IPS, network security monitoring, custom rules, log analysis, and integration with Wazuh for enhanced Blue Team cybersecurity.
Disk Analysis with Autopsy - HackerSploit Blue Team Training
Learn disk analysis using Autopsy, a digital forensics platform. Explore data sources, artifacts, and timelines for effective computer investigations. Gain practical skills in digital forensics and cybersecurity.
Moving the Industry Forward - The Purple Team Approach
Explore innovative strategies for advancing cybersecurity through the Purple Team approach, blending offensive and defensive tactics to enhance overall security posture.
Purple Team Strategies for Application Security
Explore purple team strategies for application security, blending red and blue team approaches to enhance vulnerability testing, automation, and security infrastructure integration.
Red Team, Blue Team, or White Cell? Trends in IT Security - AppSec EU 2015
Explore trends in IT security, comparing red team, blue team, and white cell approaches, and how security must adapt to function like an immune system.

Security Onion 2 Release Announcement and Live Demo
Discover the latest features and improvements in Security Onion 2 through an in-depth release announcement and live demonstration, showcasing advanced capabilities for network security monitoring and threat detection.
Red, Blue, and Purple AI - Augmenting Cybersecurity Teams with Practical AI Tools
Explore practical AI tools for red, blue, and purple teams in cybersecurity. Learn strategies to empower your security team with AI-driven solutions and create effective prompts for various security tasks.
Detection as Code - Buzzword or Panacea?
Explore the reality of Detection-as-Code in cybersecurity. Separate hype from facts and understand its potential benefits for blue teams and threat detection programs.
The Hacker Hippocampus: Meet Your Brain on Games
Explore the history and impact of gamification in infosec, its effects on brain stimulation, and how it's revolutionizing learning and skill development for security professionals.
Turning Engineers into Extended Blue Team Members - Security Strategies
Strategies for empowering engineers to become part of the security team, including threat modeling, incident-driven learning, and security testing integration into development processes.
TL;DR: Applying AI to Security - Condensed Overview of AI Applications in Cybersecurity
Explore AI's impact on security: AppSec, red/blue team tactics, threat modeling. Condenses extensive research into practical applications for rapid understanding of AI in cybersecurity.
Operationalized Purple Teaming - Red Zone Space
Learn to operationalize collaboration between security teams, improving threat detection and response through Purple Team exercises. Explore practical techniques for maturing your security program using real-world examples.
I'm Not Pink, I Prefer Purple
Exploración del Purple Team en ciberseguridad: interacción Red Team vs Blue Team, Pirámide del dolor, integración del Framework Mitre & Attack y aprovechamiento del modelo Purple Team para mejorar la seguridad.
Looking Forward - Finding the Right Balance for INFOSEC
Exploring the future of cybersecurity, balancing technology and talent, and addressing challenges in the industry through automation, red teaming, and strategic focus.
Go Purple! Adopt Purple Team Strategy to Augment Application Security Programs
Explore purple team strategies to enhance app security programs, bridging defensive and offensive approaches for effective collaboration and improved security outcomes.
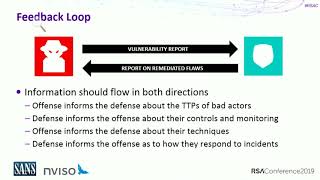
Live Adversary Simulation - Red and Blue Team Tactics
Explore live adversary simulation techniques, enhancing communication between red and blue teams for effective cybersecurity. Learn to perform threat simulations, map APT phases, and implement purple teaming strategies.