XML Out-of-Band Data Retrieval
Explore innovative XML out-of-band data retrieval techniques for accessing files and resources from victim's machines, even with normal output from vulnerable applications.
Practical Exploitation Using A Malicious Service Set Identifier - SSID
Explore SSID exploitation techniques for wireless device attacks, including XSS, CSRF, and command injection. Learn about limitations, risk factors, and see live demonstrations of these methods.
To Dock or Not to Dock - Using Laptop Docking Stations as Attack Platforms
Explore laptop docking stations as potential attack platforms, examining vulnerabilities, demonstrating covert hardware implants, and discussing detection and mitigation strategies for corporate environments.
The Sandbox Roulette - Are You Ready For The Gamble?
Explore application sandbox vulnerabilities and evasion techniques through a "Sandbox Roulette" demonstration, comparing various commercial solutions and their effectiveness against different exploit vectors.
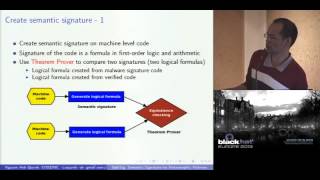
OptiSig - Semantic Signature for Metamorphic Malware
Explore semantic signatures for detecting metamorphic malware, overcoming limitations of traditional pattern matching. Learn about OptiSig toolset for generating and evaluating signatures on Intel platforms.
Practical Attacks Against MDM Solutions
Explore novel proof-of-concept attack techniques on Android and iOS devices that bypass traditional mobile malware detection and circumvent common Mobile Device Management features.
The M2M Risk Assessment Guide - A Cyber Fast Track Project
Comprehensive guide for assessing and mitigating security risks in Machine-to-Machine (M2M) technologies across industries, focusing on vulnerabilities and design strategies.
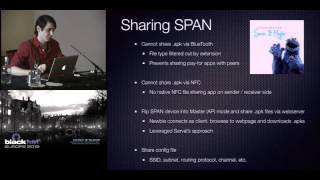
Off Grid Communications with Android - Meshing the Mobile World
Explore Android mesh networking for resilient, infrastructure-free communication. Learn to implement off-grid concepts, secure networks, and overcome hardware limitations in smartphone ad-hoc networking.
Invisibility Purge - Unmasking the Dormant Events of Invisible Web Controls
Unmasking dormant events in server web controls through refined methodology and new tool, bypassing security measures to exploit hidden application features.
Let's Play - Applanting
Discover a new attack methodology called APPLANTING, which allows attackers to install apps on Android devices without user knowledge, combining CSRF and clickjacking techniques.
Hybrid Defense - How to Protect Yourself From Polymorphic 0-days
Hybrid approach for early detection of unknown 0-day exploits at network level, combining shellcode detection algorithms to optimize classification, reduce false positives, and increase throughput.
The Deputies Are Still Confused
Exploring misunderstandings and vulnerabilities in same-origin policy, with practical examples of attacks bypassing common content-isolation mechanisms for CSRF, clickjacking, and NTLM protection.
Hardening Windows 8 Apps for the Windows Store
Explore security considerations for Windows 8 Store apps, covering HTML5, backend services, cloud computing, and WinRT to ensure robust and privacy-focused mobile development.
Honeypot That Can Bite - Reverse Penetration
Explore aggressive honeypot techniques for de-anonymizing attackers, assessing skill levels, and gaining control. Learn real-world applications and effectiveness through case studies and practical examples.
Next Generation Mobile Rootkits
Explore advanced mobile rootkit techniques using ARM TrustZone, including implementation, hiding methods, and lessons learned from creating an actual rootkit.
Multiplayer Online Games Insecurity
Explore vulnerabilities in multiplayer online games, including game-specific issues, Steam Browser Protocol security, and a new 0-day vulnerability in a popular game.
Hacking Video Conferencing Systems
Explore vulnerabilities in high-end videoconferencing systems, focusing on Polycom HDX devices. Learn about firmware analysis, device rooting, and remote exploitation techniques for H.323 protocol.
SSL Future Authenticity
Exploring SSL's history, current authenticity issues, recent infrastructure attacks, and potential solutions, with a focus on fixing trust relationships in this fundamental protocol.
Floating Car Data from Smartphones
Exploring smartphone-based traffic data: privacy implications, location tracking, and potential vulnerabilities in navigation systems. Presents a protocol to enhance security and protect user privacy.
Harnessing GPUs - Building Better Browser Based Botnets
Explore browser-based botnets using GPUs for powerful computations. Learn about XSS, HTML5, and WebGL techniques to create efficient, cross-platform botnets capable of breaking strong encryption and impacting cybersecurity.
Web Application Brute Forcing 101
Learn techniques for web application brute forcing, exploring vulnerabilities and security measures to protect against unauthorized access attempts.