Saving Cyberspace
Explore threats to internet resilience and freedom, and innovative strategies for empowering defenders to safeguard cyberspace's future against surveillance, attacks, and systemic failures.
The Defense Rests - Automation and APIs for Improving Security
Explore automation and APIs for enhancing security through centralized management, testing, and evidence-driven approaches. Learn to leverage open-source tools and protocols for efficient vulnerability detection and faster recovery.
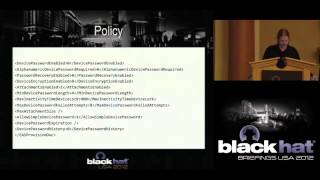
Exchanging Demands
Explore vulnerabilities in Microsoft Exchange's mobile device management, focusing on remote wipe functionality and potential exploitation through policy updates without authentication.
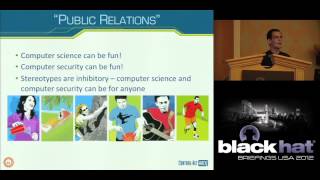
Control-Alt-Hack - White Hat Hacking for Fun & Profit
Explore ethical hacking through a card game that simulates security audits and consulting. Learn about diverse hacking skills, mission challenges, and cybersecurity concepts in an engaging, entertaining format.
Libinjection - A C Library for SQLI Detection and Generation Through Lexical Analysis
Innovative C library for SQL injection detection using lexical analysis, offering high precision and accuracy. Trained on real attacks, it categorizes threats and provides templates for new attack detection.
State of Web Exploit Toolkits
Deep dive into popular web exploit toolkits, analyzing construction, shellcodes, obfuscations, and exploits. Explore trends, data harvesting methods, and emerging players in cybercriminal landscape.
Intrusion Detection Along the Kill Chain - Why Your Detection System Sucks
Explore advanced intrusion detection techniques using the attacker plane and kill chain concepts to improve cybersecurity effectiveness beyond traditional vendor solutions.
Passive Bluetooth Monitoring in Scapy
Explore passive Bluetooth monitoring in Scapy using Python extensions and Ubertooth dongle, enabling interactive observation and development of Bluetooth auditing and pentesting tools.
Web Tracking For You
Explore advanced web tracking techniques for identifying and monitoring potential security threats, covering active and passive fingerprinting, user unmasking, and cross-platform implementation.
iOS Application Security Assessment and Automation - Introducing SIRA
Automated iOS app security assessment tool SIRA demonstrated, revealing common flaws in AppStore products. Explores risks, testing methods, and future improvements for mobile app security.
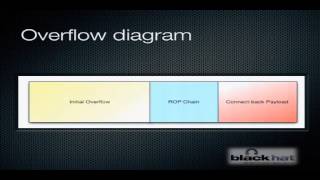
SQL Injection to MIPS Overflows - Rooting SOHO Routers
Explore SQL injection techniques to exploit buffer overflows and gain root access to Netgear routers, including file extraction and live demonstration of vulnerabilities in SOHO devices.
Ghost is in the Air - Traffic - Security Aspects of ADS-B and "Flying" Technology
Explore security vulnerabilities in ADS-B technology and potential threats to air traffic control systems, including practical demonstrations of data injection and visualization techniques.
Legal Aspects of Cyberspace Operations
Explore legal frameworks for cyberspace operations, including network security, defense, exploitation, and attack. Gain insights into recent incidents and their legal classifications.
Easy Local Windows Kernel Exploitation
Discover reliable techniques for exploiting common local Windows kernel vulnerabilities across multiple versions, including previously challenging exploits.
Torturing OpenSSL
Explore hardware vulnerabilities in secure systems through a side-channel attack on RSA signatures, demonstrating how induced faults can compromise software-secure systems and extract private keys.
Sexy Defense - Maximizing the Home-field Advantage
Proactive defense strategies: intelligence gathering, modeling, and expanding defender roles. Maximize existing resources for effective security posture against penetration testers and red teams.
PRNG Pwning Random Number Generators in PHP Applications
Techniques for exploiting randomness vulnerabilities in PHP applications, focusing on password reset token predictability and demonstrating account takeover through PRNG prediction.
How Analysis of EC Consumption of Embedded Systems Could Lead to Code Reversing
Practical approach to reverse engineering embedded systems through power analysis. Explores experimental protocol, tools, and techniques for extracting code without physical access to internal components.
Exploiting the Jemalloc Memory Allocator - Owning Firefox's Heap
Explore jemalloc memory allocator's architecture, attack vectors, and novel exploitation techniques, focusing on Mozilla Firefox's heap and its security implications.
Targeted Intrusion Remediation - Lessons From The Front Lines
Explore strategies for combating persistent cyber threats, focusing on inhibiting attacker activities, enhancing detection capabilities, and improving rapid response techniques for effective intrusion remediation.
Owning Bad Guys and Mafia with Javascript Botnets
Explore mitm attacks on anonymous services and learn to create JavaScript botnets for analyzing connections, uncovering activities of malicious actors behind these services.