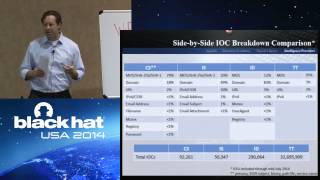
Threat Intelligence Library - A New Revolutionary Technology to Enhance the SOC Battle Rhythm
Explore the evolution of cyber threat intelligence and its impact on SOC operations. Learn about threat libraries, their importance in managing IOCs, and strategies for enhancing adversary hunting workflows.
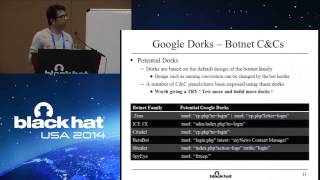
What Goes Around Comes Back Around - Exploiting Fundamental Weaknesses in Botnet C&C Panels
Explore techniques for exploiting vulnerabilities in botnet command and control panels, including detection methods, reverse attacks, and automated tools for gathering intelligence.
Prevalent Characteristics in Modern Malware
Explore prevalent characteristics in modern malware, including evasion techniques, anti-analysis methods, and defensive capabilities. Learn to improve malware prevention and analysis strategies.
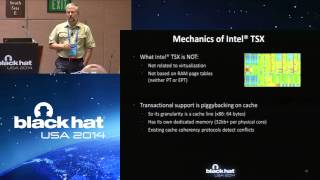
Creating a Spider Goat - Security with Intel CPU Transactional Memory Support
Explore how Intel CPU's Transactional Synchronisation Extension can enhance security by detecting and reversing unauthorized memory changes, with practical scenarios and demonstrations.

Reverse-Engineering the Supra iBox - Exploitation of a Hardened MSP430-Based Device
Detailed walkthrough of reverse-engineering and exploiting a hardened MSP430-based key storage device, covering firmware extraction, crypto analysis, and various attack techniques.
Full System Emulation - Achieving Successful Automated Dynamic Analysis of Evasive Malware
Explore full system emulation for dynamic malware analysis, addressing evasion techniques and solutions. Learn to design effective sandboxes and extract valuable intelligence from malicious files.
Exposing Bootkits with BIOS Emulation
Explore techniques to detect and counter bootkits using BIOS emulation, low-level anti-rootkit methods, and heuristic detection logic for enhanced system security and intruder defense.
The New Scourge of Ransomware - A Study of CryptoLocker and Its Friends
Explore the evolution of ransomware, focusing on CryptoLocker and its impact. Learn about threat intelligence responses, infrastructure tracking, and lessons for managing emerging cyber threats.

Find All the Badness, Collect All the Things
Explore GRR, an open-source remote live-forensics system for rapid incident response and large-scale threat hunting. Learn about artifact collection, fleet-wide analysis, and future developments in digital forensics.
One Packer to Rule Them All
Explore advanced packing techniques to evade antivirus detection, including new methods for x86 and x64 malware. Learn about static, emulation, and runtime detection stages and how to bypass them.
A Journey to Protect Points-of-Sale
Explore point-of-sale vulnerabilities, memory scraping threats, and effective mitigation strategies in retail environments. Learn practical cybersecurity measures to protect sensitive transaction data.
Why You Need to Detect More Than Pass-the-Hash
Explore advanced techniques for detecting compromised credentials beyond Pass-the-Hash, focusing on efficient methods to identify misused or stolen login information.
Investigating PowerShell Attacks
Explore techniques used by attackers to exploit PowerShell for command-and-control, lateral movement, and persistence. Learn to collect and interpret forensic evidence from real-world incidents.
Secure Product Development
Explore hardware security validation techniques, Verilog vulnerabilities, and bug resolution methods in open-source core designs. Learn to identify and address security issues in integrated circuits.
How to Wear Your Password
Innovative smart bracelet authentication system combining security and user-friendliness. Explores physical tethering, credential management, and various usage scenarios for seamless identity verification.
APT Attribution and DNS Profiling
Explore APT attack patterns through DNS profiling, utilizing automated data collection and visualization tools to identify attacker behaviors and potential identities.
Bitcoin Transaction Malleability Theory in Practice
Explore the mysterious "Transaction Malleability" vulnerability that nearly collapsed Bitcoin, with practical demonstrations of its exploitation and impact on major platforms.
Exploiting Unpatched iOS Vulnerabilities for Fun and Profit
Discover techniques for exploiting iOS vulnerabilities, including finding new attack vectors, chaining vulnerabilities, and defeating code signing to jailbreak the latest iOS version.
Write Once, Pwn Anywhere
Explore advanced Windows exploitation techniques, including DEP and ASLR bypass methods, for enhanced system penetration. Learn OS-independent strategies for more effective and versatile attacks.
Thinking Outside the Sandbox - Violating Trust Boundaries in Uncommon Ways
Explore uncommon techniques for bypassing browser sandboxes, focusing on four successful Pwn2Own contest entries. Learn about innovative attack vectors and their implications for application security.
Stay Out of the Kitchen - A DLP Security Bake-Off
Explore flaws in Data Loss Prevention solutions, including administrative interfaces and inspection engines. Learn about vulnerabilities in DLP systems and their potential for bypass.