Incident Response at Scale - Building a Next Generation SOC
Explore strategies for automating incident response processes in large-scale environments to improve efficiency, visibility, and organizational protection.
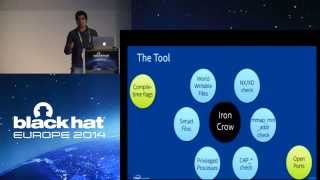
Android Kernel and OS Security Assessment with Iron Crow
Discover Iron Crow: a powerful tool for Android BSP developers and OEMs to detect platform-level vulnerabilities, enhancing security and protecting end users from potential exploits in customized Android environments.
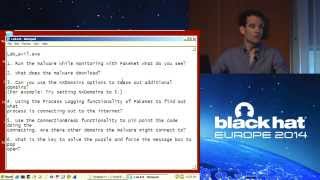
Counterfeiting the Pipes with FakeNet 2.0 - Part 2
Learn to simulate networks for malware analysis using FakeNet 2.0. Capture network signatures, mimic protocols, and defeat malware through hands-on challenges with real-world samples.
Sidewinder Targeted Attack Against Android in the Golden Age of Ad Libs
Explores vulnerabilities in Android apps and ad libraries, demonstrating a targeted attack method that exploits location data and system weaknesses to compromise user privacy and device security.
Detecting Vulnerabilities in Virtual Devices with Conformance Testing
Explore techniques for detecting vulnerabilities in virtual devices using conformance testing, enhancing security in virtualized environments.
Shattering Illusions in Lock-Free Worlds - Compiler - Hardware Behaviors in OSes - VMs
Explores memory access issues in multi-threaded environments, focusing on compiler/hardware behaviors that can lead to security vulnerabilities in OSes, VMs, and applications.
Industroyer - Crashoverride - Zero Things Cool About a Threat Group Targeting the Power Grid
Análisis detallado del malware Industroyer utilizado en el ciberataque a la red eléctrica de Ucrania en 2016, sus capacidades y el grupo de amenazas detrás del ataque.
The UEFI Firmware Rootkits - Myths and Reality
Explore UEFI firmware security, vulnerabilities, and real-world applicability of attacks. Analyze rootkit scenarios and assess practical implications for system compromise at privileged levels.

Techniques to Gather Threat Intel and Track Actors
Discover 24 techniques for gathering threat intelligence and tracking actors, illustrated with 30 real-world cases. Learn about crimeware vulnerabilities, C&C misconfigurations, and underground marketplaces.
Go Get My - Vulnerabilities - An In-Depth Analysis of Go Language Runtime and the New Class of Vulnerabilities It Introduces
Explore Go language runtime vulnerabilities, their impact on applications, and potential security risks in this in-depth analysis of Golang's growing adoption across various programming domains.
Real-World Post-Quantum Cryptography - Introducing the OpenQuantumSafe Software Project
Explore OpenQuantumSafe, an open-source library for quantum-safe cryptography, including implementations, benchmarks, integration challenges, and future developments.
Hello From the Other Side - SSH Over Robust Cache Covert Channels in the Cloud
Explore practical cache covert channels in cloud environments for secret data exfiltration between isolated virtual machines, presented by security researchers at Black Hat Asia.

Testing Vehicles with CANToolz
Explore CANToolz framework for CAN bus analysis, featuring black-box testing of automotive networks and ECUs. Learn practical use-cases for vehicle security research and penetration testing.
Bypassing Secure Boot Using Fault Injection
Explore fault injection techniques to bypass Secure Boot in embedded systems, focusing on hardware-based attacks when logical vulnerabilities are absent.
Mobile Espionage in the Wild - Pegasus and Nation-State Level Attacks
Explore Pegasus, a sophisticated mobile espionage tool, its technical capabilities, and real-world impact. Learn about infrastructure tracking and malware detection in high-profile attacks.
Effective File Format Fuzzing – Thoughts, Techniques and Results
Explore advanced file format fuzzing techniques for vulnerability hunting, including setup, scalability, and achieving optimal results against modern software.
Breaking Big Data - Evading Analysis of the Metadata of Your Life
Explore techniques to protect your digital privacy and evade metadata analysis in an era of pervasive surveillance by governments and corporations.
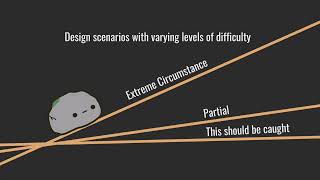
Blue to Red - Traversing the Spectrum
Explore the importance of foundational security skills and an adversarial mindset in navigating diverse InfoSec roles, from forensics to red teaming, in this insightful keynote by Amanda Rousseau.
Breaking Encrypted Databases - Generic Attacks on Range Queries
Explore generic attacks on encrypted databases supporting range queries, focusing on common building blocks and latest solutions in commercial and academic settings.
How Do Cyber Insurers View The World
Insider perspective on cyber insurance: company assessments, pricing, claims, and industry evolution. Gain insights into how insurers evaluate and manage cyber risks.
Rogue7 - Rogue Engineering-Station Attacks on S7 Simatic PLCs
Uncovers vulnerabilities in Siemens S7 PLC systems, demonstrating potential attacks on industrial control architectures despite claimed security measures and advanced cryptographic protocols.