Sleight of ARM - Demystifying Intel Houdini
Explore Intel's Houdini binary translator for running ARM on x86, its architecture, security implications, and comparison with Apple's Rosetta 2, focusing on Android emulation and Chromebooks.
The Case for a National Cybersecurity Safety Board
Explores the need for a National Cybersecurity Safety Board to investigate and prevent cyber attacks, drawing parallels with the NTSB and addressing critical infrastructure vulnerabilities.
President's Cup Cyber Competition - Finding the Best Cyber Talent in the US Government
Explore the behind-the-scenes story of the President's Cup Cybersecurity Competition, designed to identify and challenge top US government cyber talent.
Bringing the Power of Symbolic Execution to the Fight Against Malicious Excel 4 Macros
Explore Symbexcel, a tool using symbolic execution to analyze and detect malicious Excel 4.0 macros, enhancing cybersecurity against this common attack vector.
The Dark Age of Memory Corruption Mitigations in the Spectre Era
Explores how speculative execution attacks can bypass memory corruption defenses, challenging established security measures and revealing vulnerabilities in modern computer systems.
Your Software IS - NOT Vulnerable - CSAF, VEX, and the Future of Advisories
Explore the future of software security advisories, focusing on CSAF and VEX, and learn how to manage the increasing volume of vulnerability information effectively.
How I Used a JSON Deserialization 0day to Steal Your Money on the Blockchain
Explore a JSON deserialization vulnerability in Fastjson, its exploitation for remote code execution, and implications for blockchain security.
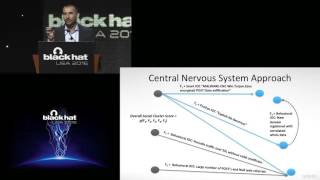
From False Positives to Actionable Analysis
Modeling human behavior in network traffic to automatically label security events, using distributed forensic AI for threat detection and response optimization.
Most Ransomware Isn't As Complex As You Might Think
Análisis de más de 1.300 muestras de ransomware revela que la mayoría no son tan sofisticados como se cree. Se discuten técnicas de detección y prevención, así como la evolución y características comunes de diferentes familias de ransomware.
Advanced IC Reverse Engineering Techniques - In Depth Analysis Of A Modern Smart Card
Explore advanced IC reverse engineering techniques through in-depth analysis of a modern smart card, focusing on hardware attacks, proprietary algorithms, and efficient analysis methods.
Automated Human Vulnerability Scanning With AVA
Explore automated human vulnerability scanning with AVA, a tool for mapping people's connectivity, testing security threats, and measuring behavior to address human security risks.
Defeating Machine Learning - What Your Security Vendor Is Not Telling You
Explore attacker strategies to defeat machine learning-based security defenses, analyze industry issues enabling these vulnerabilities, and discover novel data sourcing solutions for improved protection.
The NSA Playset - A Year of Toys and Tools
Explore NSA-inspired gadgets for USB, PCI Express, I2C, GSM, Bluetooth, and RF retroreflectors. Learn about tools mimicking intelligence agency capabilities for electronic device eavesdropping and surveillance.
Defeating Pass-the-Hash - Separation of Powers
Explore Windows 10's innovative approach to defeating Pass-the-Hash attacks through strong isolation of symmetric credentials, leveraging virtualization technology to sequester secrets from potential attackers.
Cloning 3G - 4G SIM Cards With A PC And An Oscilloscope - Lessons Learned In Physical Security
Reveals vulnerabilities in 3G/4G SIM cards, demonstrating how to clone them using differential power analysis. Discusses implications for mobile network security and showcases practical experiments.
Abusing Windows Management Instrumentation - WMI
Explore WMI's potential for stealthy, persistent attacks on Windows systems. Learn offensive techniques, backdoor creation, and defense strategies against WMI-based threats.
Remote Exploitation of an Unaltered Passenger Vehicle
Comprehensive exploration of remote vehicle hacking, demonstrating real-world attacks on unaltered cars and pivoting through hardware to send CAN bus messages affecting critical systems.

Red Vs. Blue - Modern Active Directory Attacks, Detection, And Protection
Explore advanced Active Directory attack methods, detection techniques for Golden and Silver Tickets, and effective mitigation strategies. Learn to identify and protect against sophisticated network intrusions.
Writing Badass Malware for OS X
Explore advanced OS X malware techniques, persistence methods, and security bypasses. Learn to create sophisticated threats and enhance Mac protection against current and future malware.
Harnessing Intelligence From Malware Repositories
Explore techniques for extracting intelligence from malware repositories using program analysis and data mining, with insights on connecting seemingly disparate cyber attacks and tracking malware trends.
Rocking the Pocket Book - Hacking Chemical Plant for Competition and Extortion
Explore techniques for exploiting chemical plant systems to cause economic damage while avoiding detection. Learn about attack stages, cost considerations, and creating misleading forensic evidence.