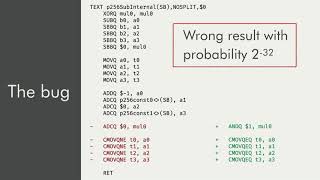
Squeezing a Key through a Carry Bit
Explore a practical key recovery attack on Go's P-256 elliptic curve implementation, targeting JSON Web Encryption through a subtle carry bit bug.
Your Voice is My Passport
Explore machine learning's impact on voice authentication security, including synthetic audio generation and potential vulnerabilities in financial and home automation systems.
Are You Trading Stocks Securely? Exposing Security Flaws in Trading Technologies
Exposing security vulnerabilities in electronic trading platforms, highlighting risks in mobile, desktop, and web applications for investors of all levels.
ARTist - A Novel Instrumentation Framework for Reversing and Analyzing Android Apps and the Middleware
Explore Android Runtime security with ARTist, a novel instrumentation framework for analyzing apps and middleware. Learn deployment, modules, and creation techniques.
Subverting Sysmon - Application of a Formalized Security Product Evasion Methodology
Explore methodologies for subverting Sysmon, a security monitoring tool, through data collector strategies and configuration analysis to enhance adversarial techniques against enterprise defenses.
I, for One, Welcome Our New Power Analysis Overlords
Introduces ChipWhisperer-Lint, an open-source tool for automating power analysis attacks on devices using ChipWhisperer hardware, enhancing security testing capabilities.
Lessons from Virginia - A Comparative Forensic Analysis of WinVote Voting Machines
Forensic analysis of WinVote machines reveals security flaws and vulnerabilities in electronic voting systems, highlighting the importance of robust election technology and auditing processes.
Two-Factor Authentication, Usable or Not? - A Two-Phase Usability Study of the FIDO U2F Security Key
Explore the usability of FIDO U2F Security Keys for two-factor authentication through a comprehensive two-phase study, evaluating effectiveness and user experience.
Decompiler Internals - Microcode
Explore the intermediate language used in Hex-Rays Decompiler, understanding its simplicity and power in representing complex programs.
The Air-Gap Jumpers
Explore covert channels for breaching air-gap isolation, including electromagnetic, acoustic, and optical methods. Learn about 'Bridgeware' malware and new air-jumping techniques.
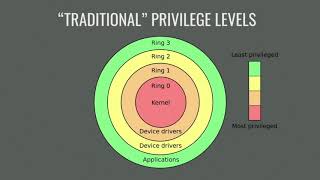
Why so Spurious? Achieving Local Privilege Escalation on Operating Systems
Explore a critical x86 architecture vulnerability exploitable for local privilege escalation across Windows, macOS, and Linux. Learn about this widespread security issue and its implications.
Disappeared Coins - Steal Hashrate in Stratum Secretly
Unveils two novel man-in-the-middle attack schemes on Stratum, the main communication protocol for cryptocurrency mining pools, potentially compromising miners' computing power.
The Cost of Complexity - Different Vulnerabilities While Implementing the Same RFC
Exploring security vulnerabilities in DNS implementations due to complexity and ambiguity in RFC 1035, focusing on message compression and its impact on TCP/IP stacks.
Hunting Vulnerabilities of gRPC Protocol Armed Mobile - IoT Applications
Explore security vulnerabilities in gRPC-powered mobile and IoT apps. Learn about common pitfalls, attack vectors, and strategies to enhance protection in this high-performance protocol.
Racing the Dark - A New TOCTTOU Story From Apple's Core
Unveils macOS kernel vulnerabilities, highlighting memory mapping issues and race conditions that bypass security updates. Emphasizes the need to reevaluate macOS/iOS memory mapping mechanisms.
We Are About to Land - How CloudDragon Turns a Nightmare Into Reality
Explore CloudDragon's advanced cyber tactics, including supply chain and cross-platform attacks. Gain insights into APT group operations and their evolving techniques in this cybersecurity analysis.
Pre-built JOP Chains with the JOP ROCKET - Bypassing DEP without ROP
Explore Jump-oriented Programming (JOP) as an alternative to ROP for code-reuse attacks. Learn about the JOP ROCKET tool for creating pre-built JOP chains to bypass DEP without ROP.
Hey, You, Get off My Private Data - Do Apps Respect Your Privacy as They Claim?
Explore multinational data protection regulations and assess app compliance. Learn about privacy policies, GDPR principles, and techniques for evaluating personal data handling in mobile applications.
Vibe Check - Why Students May Shy Away From Cyber in a Surveillance State
Explores impact of surveillance and strict laws on cyber talent in Asia Pacific, discussing challenges for ethical hacking and threat research in a censorship-heavy environment.
A Mirage of Safety - Bug Finding & Exploit Techniques of Top Android Vendor's Privacy Protection Apps
Uncovers vulnerabilities in popular Android privacy protection apps, revealing security flaws and exploit techniques. Offers insights on improving mobile data security and privacy safeguards.
Alarm.DISARM - Remotely Exploiting & Disarming Popular Physical Security System from Public Internet
Explore remote code execution vulnerabilities in physical security systems, learning to exploit and disarm alarms through reverse engineering and network protocol analysis.