Same Origin Method Execution - Exploiting a Callback for Same Origin Policy Bypass
Explore a powerful web attack technique that exploits JSONP to bypass Same Origin Policy, potentially compromising entire domains without user interaction or typical browser protections.
Bypassing HTTP Strict Transport Security
Explore vulnerabilities in HTTP Strict Transport Security (HSTS) and learn how attackers can exploit inter-operation weaknesses to bypass this protection and launch SSLStrip attacks.
APTs Way - Evading Your EBNIDS
Explore advanced techniques for evading Emulation Based Network Intrusion Detection Systems, covering preprocessing, emulation, and heuristic detection evasion methods used by sophisticated attackers.
Cellular Exploitation on a Global Scale - The Rise and Fall of the Control Protocol
Explore hidden cellular device controls, their vulnerabilities, and potential for global exploitation. Learn reverse engineering techniques and gain insights into Over-the-Air code execution across major platforms.
Windows Kernel Graphics Driver Attack Surface
Explore the attack surface of Windows graphics drivers, including exposed ioctl's, driver internals, and security implications for researchers and developers.
Abusing Microsoft Kerberos - Sorry You Guys Don't Get It
Explore Kerberos vulnerabilities in Microsoft Active Directory, revealing long-term security risks and challenging assumptions about authentication protocols.
MoRE Shadow Walker - The Progression of TLB-Splitting on x86
Explore TLB-splitting evolution on x86 architecture, from defensive memory protections to offensive rootkit techniques. Learn new methods for modern processors and their implications for cybersecurity.
Computrace Backdoor Revisited
Exposición de vulnerabilidades en software antirrobo Computrace, demostrando fallos de seguridad y posibles ataques. Incluye análisis del protocolo, comportamiento sospechoso y métodos de detección/desactivación.
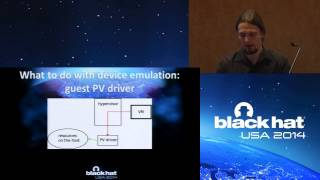
Poacher Turned Gamekeeper - Lessons Learned from Eight Years of Breaking Hypervisors
Explore hypervisor vulnerabilities, attack surfaces, and security design flaws through real-world examples. Learn key lessons for improving hypervisor security and hardening techniques.
Understanding TOCTTOU in the Windows Kernel Font Scaler Engine
Explore TOCTTOU vulnerabilities in Windows Kernel Font Scaler Engine, covering basic double fetch issues, stealthy design flaws, and their impact on system security. Learn about font file manipulation and exploit techniques.
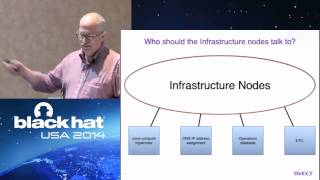
OpenStack Cloud at Yahoo Scale - How to Avoid Disaster
Learn strategies to secure large-scale OpenStack deployments, including hardening techniques, compromise mitigation, and network architecture considerations, based on Yahoo's experience managing massive cloud infrastructure.
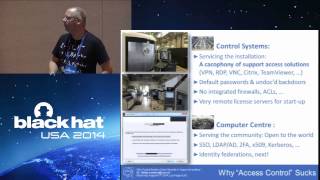
Why Control System Cyber-Security Sucks
Explores challenges in industrial control system cybersecurity, critiquing current approaches and advocating for a paradigm shift towards standardized IT practices and people-centric solutions.
Next Generation Disassembly Framework
Explore next-gen disassembly framework for multi-architecture binary analysis. Learn about Capstone engine's features, design challenges, and potential applications in reversing, exploit development, and malware detection.
The Big Chill - Legal Landmines that Stifle Security Research and How to Disarm Them
Legal challenges and risks in security research: exploring laws, cases, and potential solutions to protect researchers while promoting cybersecurity advancements.
A Scalable, Ensemble Approach for Building and Visualizing Deep Code-Sharing Networks
Innovative ensemble approach for detecting code-sharing in malware, combining multiple analysis techniques to overcome obfuscation and scale to millions of samples. Includes visualization and open-source implementation.
Nobody is Listening to Your Phone Calls - Really - A Debate and Discussion on the NSA's Activities
Debate on NSA surveillance activities, exploring privacy concerns, legal implications, and national security arguments. Experts discuss the scope and impact of data collection programs on citizens' rights.
Miniaturization
Exploring advanced SCADA hacking techniques, focusing on miniaturization challenges in embedded devices and novel algorithms for stealthy attacks on industrial control systems.

ICSCorsair - How I Will PWN Your ERP Through 4-20 mA Current Loop
Explore vulnerabilities in industrial control systems, from low-level protocols to high-level applications. Learn about ICSCorsair, an open hardware tool for auditing and exploiting ICS networks across multiple layers.
The Node.js Highway - Attacks Are At Full Throttle
Explore Node.js security issues and effective measures for secure application development. Learn about weak cryptography, testing, MongoDB, and see a practical demo.
The Little Pump Gauge That Could - Attacks Against Gas Pump Monitoring Systems
Explore attacks on gas pump monitoring systems, their vulnerabilities, and the motives behind them. Learn about honeypot deployment and prevention strategies.
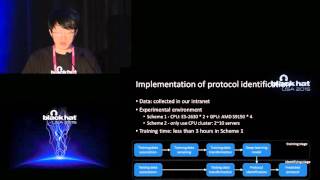
The Applications of Deep Learning on Traffic Identification
Explore deep learning for network traffic identification, covering neural networks, automatic feature learning, and anomaly detection. Improve protocol identification beyond traditional methods.