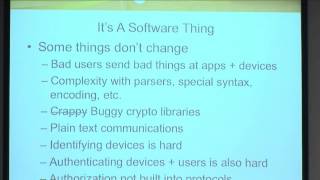
MQTT and CoAP - A Story about IoT Protocol Security
Explore MQTT and CoAP protocols for IoT, their security challenges, and mitigation strategies. Learn about common architectures, potential attacks, and best practices for secure implementation.
Mitigating LangSec Problems With Capabilities
Explore how capability-based systems like Sandstorm mitigate language-based security vulnerabilities through robust isolation and authorization mechanisms, enhancing web application security.
Spring Security for N00bz - A Quick Introduction for the Terminally Insecure
Comprehensive introduction to Spring Security, covering defense-in-depth strategies and live coding demonstrations for securing applications using open-source tools.
Writing a Massive Angular App at Google
Explore technical challenges and solutions for large AngularJS apps, including code reuse patterns, custom server communication, authorization, and conditional feature loading.
Selecting the Right Identity Provider for Kubernetes - A Comparative Survey
Comparative analysis of identity providers for Kubernetes, covering authentication, authorization, user management, and federation. Helps attendees choose the right solution for their workloads.
VPN Architectures - Looking at the Complete Picture
Comprehensive exploration of VPN architectures, addressing enterprise security concerns, integration with authorization systems, and deployment strategies for branch offices and remote users.
Building a Backend-less URL Shortener
Learn to build a serverless URL shortener using only YAML, integrating authorization and a database for scalability while reducing latency and costs. Explore gateway-based business logic and security.
Designing APIs for 150 Million Orders
Strategies for designing scalable APIs to handle high-volume orders, focusing on DDD, microservices, and frontend best practices like BFF and SSR for modern, distributed systems.
The Secrets of OAuth 2.0 Part 1/2
Explore OAuth 2.0's history, differences from OAuth 1, authentication vs. authorization, grant types, token management, and PKCE in this expert interview on secure API access.
Appsec TLDR
Explore web application security essentials, including browser proxies, HTTP requests, cookies, and common vulnerabilities like XSS and SQL injection. Learn attacker mentality and defense strategies.
OWASP Mobile Top Ten - Why They Matter and What We Can Do
Explore OWASP Mobile Top Ten vulnerabilities, their significance, and strategies for mitigation. Learn about transport layer protection, threat modeling, and best practices for mobile app security.
Securing ASP.NET Core Web Apps
Learn essential techniques for securing ASP.NET Core web applications, covering vulnerability management, authorization, data protection, CSRF prevention, and protection against common attacks.
API Security Tokens Flows and the Big Bad Wolf
Explore API security, authorization flows, and authentication methods to protect digital resources from potential threats and ensure secure access in modern applications.
How to Develop Your First Cloud-Native Applications with Java
Learn to create, deploy, and run microservices using JavaEE, Eclipse MicroProfile, Kubernetes, and Istio. Explore key cloud-native application features and hands-on development with open-source example code.
The Security Evolution of gRPC Services in the Mesh
Explore the evolution of securing gRPC services in containers and service mesh, focusing on Istio's role in enhancing security for east-west traffic without sidecar complexity.
SEVEN Things About API Security
Discover essential API security practices, covering authentication, authorization, data protection, and threat mitigation strategies for robust and secure API development.
OAuth2, OpenID - Live Coding SSO, from First Principles
Live coding demonstration of implementing Single Sign-On (SSO) using OAuth2 and OpenID protocols, exploring fundamental concepts and practical application techniques.
IPVM - Seamless Services for an Open World
Explore IPVM and UCAN Invocation for next-gen open services with location-free verifiable data and computation, enabling seamless interoperability and improved scaling in decentralized applications.
Architecture Deep Dive in Spring Security
Architectural deep dive into Spring Security, focusing on authentication and authorization. Empowers developers with in-depth knowledge and demonstrates various security scenarios.
Easily Secure and Add Identity Management to Your Spring - Boot Applications
Discover KeyCloak for secure identity management in Spring Boot applications through interactive live coding. Learn to implement authentication and authorization effortlessly using the Spring Boot adapter and Spring Security integration.

Next Generation OAuth Support with Spring Security 5
Explore OAuth 2.0 and OpenID Connect 1.0 support in Spring Security 5, focusing on OAuth 2.0 Login feature implementation and custom user authority mapping for enhanced authorization.