Beyond the MCSE - Active Directory for the Security Professional
Comprehensive exploration of Active Directory's critical components, security features, and vulnerabilities, empowering security professionals to better defend enterprise resources against sophisticated attacks.
OAuth for Beginners
Einführung in OAuth: Funktionsweise, Vorteile und Implementierungstipps für Entwickler. Grundlegende Konzepte und Best Practices für sichere Authentifizierung und Autorisierung in Webanwendungen.
On the Security and Usability of Segment-based Visual Cryptographic Authentication Protocols
Explores security and usability of segment-based visual cryptographic authentication, analyzing protocols for effectiveness in balancing protection and user experience.
Signing Me onto Your Accounts through Facebook and Google - A Traffic-Guided Security Study of Commercially Deployed Single-Sign-On Web Services
Explores security vulnerabilities in popular web-based single sign-on systems, uncovering critical flaws that allow unauthorized access to user accounts on major platforms.
Economics, Physics, Psychology & Relation to Technical Aspects of Counter Intelligence
Explore economic, physical, and psychological aspects of counter-intelligence, examining authentication protocols, learned helplessness, and interactive risk in cybersecurity.
Do You Really Know JWT?
Explore lesser-known aspects of JSON Web Tokens, including implementations beyond JWS, and their practical applications in authentication and information transmission.
Understanding OAuth2 for Real
Explore OAuth2 protocol flows and implement a secure OAuth2 Flow with practical insights and theoretical overview from Johannes Pichler's expert session.
Lost in OAuth - Learn Velruse and Get Your Life Back
Explore Velruse, a Python library simplifying OAuth implementation for seamless third-party authentication in web applications. Gain practical insights to streamline your development process.
Service Interoperability With gRPC
Explore Salesforce's gRPC-based solution for standardized service communication, including implementation details and future plans for reactive streams integration.
Modern Authentication
Unravel modern authentication concepts like OAuth, OpenIDConnect, and tokens. Learn how to implement secure, distributed application access without sharing passwords.
Signing Into One Billion Mobile App Accounts Effortlessly with OAuth2.0
Explore vulnerabilities in OAuth2.0 protocol when used for mobile app authentication, uncovering potential security risks in Single-Sign-On services for billions of users.
RG Nets rXg Control Plane - Network Access and Subscriber Services Automation
Discover how rXg platform automates network access control, subscriber services, and authentication through intuitive portals, enabling non-technical staff to manage complex network operations efficiently.
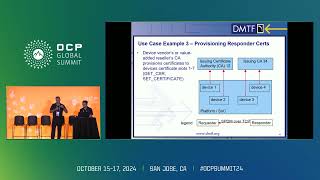
Security Protocol and Data Model (SPDM) for TCP Transport - Implementation and Use Cases
Explore SPDM protocol implementation over TCP transport, covering authentication, attestation, and security features for device communication and connection establishment models.
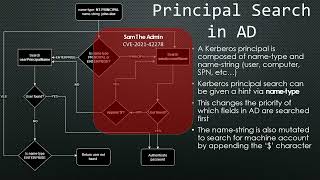
Abusing Mixed Vendor Kerberos Stacks - Exploiting Windows AD and Linux Authentication
Discover security vulnerabilities in mixed Kerberos environments and learn how to exploit weaknesses between Windows Active Directory and Linux/Unix systems for privilege escalation.
Federated Authentication in Headless Environments - SAML and OIDC Implementation Challenges
Explore OIDC authentication implementation in headless environments, focusing on OpenStack client integration, security flows, and practical solutions for CLI-based authentication challenges.
Windows Hello for Business Security Analysis and Authentication Protocol Deep Dive - Lecture 10
Explore Windows Hello for Business authentication internals, security vulnerabilities, and attack vectors in Azure AD environments, focusing on key provisioning and credential management.
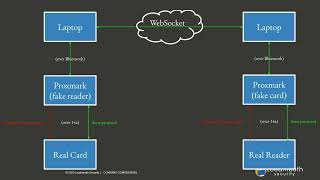
Unlocking Doors Through Long-Range Relay Attacks on Contactless Credentials
Discover how to execute long-range relay attacks on contactless credentials through ISO 14443A protocol vulnerabilities, including live demonstrations and practical mitigation strategies.
Spooky Authentication at a Distance - Post-exploitation Techniques for Windows Environments
Discover innovative post-exploitation techniques for proxying Windows authentication protocols remotely, enabling user impersonation and domain control without elevated privileges.
NTLM Authentication Vulnerabilities and Exploits - A Final Analysis
Dive into critical NTLM authentication vulnerabilities, exploring new bugs, bypass techniques, and security control gaps in Windows systems before Microsoft phases out this protocol.
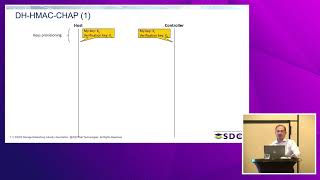
Scaling NVMe Over IP Fabric Security - Making Authentication Simple and Deployable
Discover how to implement scalable security solutions for NVMe over IP fabrics through authentication methods, TLS channels, and Authentication Verification Entity deployment.
A Decade of Active Directory Attacks: What We've Learned and What's Next
Explore a decade of Active Directory attacks, lessons learned, and future trends in this insightful IT security talk by Sean Metcalf at TROOPERS24 conference.