Attacks From a New Front Door in 4G & 5G Mobile Networks
Unveils critical API vulnerabilities in 4G/5G networks, exposing risks for AI, MEC, and IoT applications. Explores attack vectors, security misconfigurations, and potential exploits in commercial providers' systems.
All Your Containers Are Belong to Us
Explore container orchestration security risks, focusing on exposed management nodes and APIs. Learn implications, recommendations, and see demonstrations of potential exploits in popular platforms.
TruffleHog Chrome Extension - Open CORS in SAAS API's Lead to Leaky Keys
Discover API keys hidden in web pages with the open-source TruffleHog Chrome extension. Learn how to use this tool and explore real-world examples of exposed keys in SaaS APIs with open CORS.
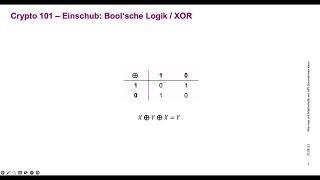
Wie man mit Mathematik ein API übernehmen kann - und wie gute Architektur das verhindert
Entdecken Sie, wie mathematische Schwachstellen in der Kryptographie zur Übernahme eines API-Gateways führen können und lernen Sie Strategien zur Verhinderung solcher Angriffe durch defensive Architektur.
How to Get Along with HATEOAS Without Letting the Bad Guys Steal Your Lunch
Explore secure HATEOAS implementation for RESTful web services, balancing design flexibility with cybersecurity. Learn practical steps to protect against exploits while leveraging dynamic client-server interactions.
Common API Security Pitfalls
Explore common API security pitfalls, their root causes, and best practices for protection. Learn to assess and improve API security for better user account and data protection.
Microservices for the Masses with Spring Boot, JHipster, and JWT
Learn to build and secure microservices using Spring Boot, JHipster, and JWT. Explore deployment options, API gateways, and modern tools like Docker and Kubernetes in this code-heavy presentation.

Securing Your APIs with OAuth 2.0
Learn to secure APIs using OAuth 2.0, covering JWT access tokens, scope design, and microservices architecture. Gain insights on authorization protocols, multi-factor auth, and backend service separation.
Attackers Want Your Data and They're Getting It From Your API
Learn techniques to protect your API from attackers, including traffic analysis, authentication methods, encryption, and advanced security measures. Gain insights into API vulnerabilities and effective countermeasures.
Common API Security Pitfalls
Explore common API security pitfalls, their root causes, and actionable solutions to protect your APIs from unauthorized access and account compromises.
Hack Like a Pro - Bug Bounties, Web Vulnerabilities & More
Explore ethical hacking, bug bounties, web vulnerabilities, and API security. Learn how to start in cybersecurity, understand ethical boundaries, and get tips for password management and bug hunting.
API Security Through External Attack Surface Management
Integrating APIs into External Attack Surface Management to improve security posture. Discover and assess exposed assets, including APIs, for better protection and risk mitigation.
What Do You Mean My Security Tools Don't Work on APIs?
Explores techniques for securing APIs and modern service-based web applications, discussing challenges and innovative approaches like security instrumentation for vulnerability identification and protection.
ARBITRAR - User-Guided API Misuse Detection
Explore user-guided techniques for detecting API misuse, enhancing software reliability and security through advanced analysis methods.
Designing Secure APIs
Improve API security design using tools and guidelines. Learn about JSON complexities, schemas, JWTs, rate-limiting, and enforcing rules with OpenAPI and static analysis tools.
How to Leak a 100-Million-Node Social Graph in Just One Week
Exploración de vulnerabilidades en OAuth 2.0 para redes sociales, demostrando cómo la suplantación de aplicaciones puede llevar a la filtración masiva de datos de usuarios y gráficos sociales.

OAuth Tokens As Your Identity API
Explore OAuth and OpenID Connect for secure, scalable identity management in distributed systems. Learn to leverage tokens for user permissions, tracing, and delegation across complex networks.
Unlock the Secrets of Great, Lasting APIs
Discover key insights on designing and building effective web APIs, including handling team friction, making technical choices, sketching, reversibility, versioning, and security considerations.
Going Static in a Dynamic World with Hasura and Nuxt.js
Explore static site development with Hasura and Nuxt.js, covering API setup, GraphQL integration, deployment triggers, and the benefits of Nuxt's static module for secure, efficient web applications.
The Secrets of OAuth 2.0 Part 1/2
Explore OAuth 2.0's history, differences from OAuth 1, authentication vs. authorization, grant types, token management, and PKCE in this expert interview on secure API access.
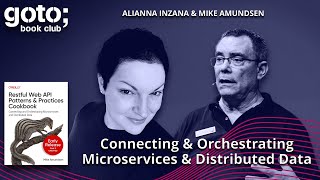
Restful Web API Patterns & Practices Cookbook
Explore the evolution of RESTful Web APIs, from design to implementation, covering security, evolvable architecture, and practical patterns for connecting microservices and orchestrating distributed data.