Introduction to Emerging JSON-Based ID and Security Protocols
Explore emerging JSON-based identity and security protocols with Brian Campbell, focusing on JOSE and its applications in modern authentication and authorization systems.
Exploiting CORS Misconfigurations for Bitcoins and Bounties
Explore CORS misconfigurations and their exploitation potential, including real-world examples of vulnerabilities in bitcoin exchanges and major websites. Learn about specification flaws and mitigation strategies.
Automating API Penetration Testing Using Fuzzapi
Explore automated API penetration testing with fuzzapi, addressing common vulnerabilities in REST APIs. Learn to integrate security testing into development pipelines for early detection and mitigation.
Building Secure Cloud-Native Applications with Spring Boot and Spring
Learn to build secure cloud-native applications using Spring Boot and Spring, focusing on best practices and techniques for robust, scalable, and protected software development.
The API Assessment Primer
Learn essential API security assessment techniques, including key considerations, testing steps, and best practices for protecting APIs and mobile applications from common vulnerabilities and threats.
Scanning with Swagger - Using the Open API Specification to Find Vulnerabilities
Explore leveraging Open API specification for enhanced security scanning, uncovering vulnerabilities and improving application protection strategies.
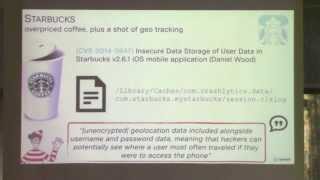
When Geo Goes Wrong - A Case Study of Geolocation Vulnerabilities in Mobile Apps
Exploring geolocation vulnerabilities in mobile apps, focusing on a dating app case study. Discusses common bugs, attack methods, and best practices for secure location-aware app development.
API Authentication's Poorly Implemented - Security Issues in Web APIs
Explore real-world API security issues, focusing on authentication and authorization problems across various platforms. Learn from examples ranging from online payment systems to embedded device infrastructures.
Kong API Gateway Integration with Okta OIDC Authentication
Integrate Kong API gateway with Okta OIDC for seamless authentication, eliminating the need for your application to manage OIDC flows directly.
Shift-Left DevOps for APIs with Okta and JFrog - Developer Day 2021
Strengthen your shift-left DevSecOps strategy by automating REST API security validation using Okta and JFrog. Learn to verify authentication and authorization policies before production release.
High-Level API Security with Keycloak - FAPI Implementation and Conformance
Explore high-level API security using Keycloak, focusing on OAuth 2.0, FAPI, and advanced features for robust authorization in digital transformation contexts.
Handling JWTs: Understanding Common Pitfalls
Explore JWT authentication, common pitfalls, and security best practices. Learn about JWT structure, verification, and protection against attacks like algorithm confusion and secret brute-forcing.
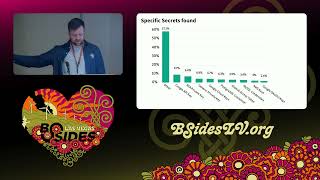
The Attacker's Guide to Exploiting Secrets in the Universe
Explore methods to discover and exploit secrets in git repositories, containers, and compiled apps. Learn about vulnerabilities in API keys and credentials across various environments.
Harmonizing OWASP API and Application Top 10 Security Risks - Combining Lists for Comprehensive Coverage
Explore API security risks, comparing OWASP's API and Application Top 10 lists. Learn detection and prevention strategies for vulnerabilities in web services, APIs, and GraphQL.
Bots Gone Phishing - Defending Against Automated Attacks and Phishing
Explore techniques to defend against phishing bots using obfuscation and one-time tokens, increasing costs for attackers while protecting web applications and APIs from automated threats.
OWASP API Security: Sufficient Logging and Monitoring for API Protection
Explore real-world examples and best practices for implementing sufficient API logging and monitoring to enhance security, observability, and incident response capabilities.
Securing Modern Applications and APIs Against Attacks
Explore effective API security strategies for modern applications, focusing on deep application knowledge and user behavior to protect against evolving threats in cloud-native architectures.
Are You Safe from OWASP #11? - Creating a Successful API Security Program
Explore API security beyond Top 10 lists, focusing on building a comprehensive program at scale. Learn key strategies for successful API protection and management.
Advanced API Security with Kong - Developer Day 2021 Labs
Learn to secure APIs using Kong Gateway and Okta. Configure OIDC authentication for Kong Developer Portal and Manager, and explore various security plugins and features.
Integrating Identity into APIs with Okta and Kong - Developer Day 2021
Discover powerful authentication and authorization scenarios using Kong and Okta. Learn to implement sophisticated API access and management flows with OIDC and OAuth, including CI/CD pipeline integration.
How to Hack an API in 15 Minutes
Discover how hackers exploit Shadow APIs to extract large volumes of data quickly. Learn about this basic yet non-obvious security vulnerability and creative methods used by attackers.