Configuring CORS in Spring Boot and Spring Security
Configure Cross-Origin Resource Sharing (CORS) in Spring Boot and Spring Security. Learn implementation at controller, method, and global levels for flexible cross-domain request authorization.
Privacy, Consent and Security Within Modern Applications
Explore privacy regulations, consent management, and security considerations in modern app development, focusing on data handling, user trust, and regulatory compliance.
OAuth2 on a National Level - How to Secure Extremely Sensitive APIs
Exploring HelseID's enhanced OAuth security profile for sharing sensitive health data across Norway's healthcare systems, addressing strict requirements and future developments.
Channeling the Potential of Generative AI with API Ecosystems
Explore innovations in Apigee API Management to accelerate development, gain control, and enhance security in generative AI-powered API ecosystems.
Three Ways to Use AI on Android - The Good, the Bad and the Ugly
Explore practical strategies for responsible AI integration in Android apps, from basic implementations to secure, cost-optimized architectures.
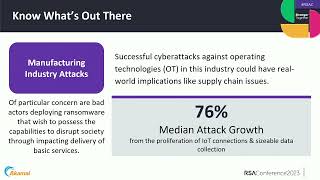
Spotlight on Latest Web Application and API Attack Data
Gain insights into global web application and API attack trends, methodologies, and tools. Analyze regional and industry-specific differences, with a focus on API security challenges.
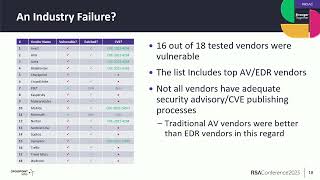
The Hidden Risk in Undocumented API Behavior
Explore undocumented Win32 API risks affecting AV and EDR vendors, potential attacks, and lessons learned for improved cybersecurity practices.
Web API Testing: Fundamentals and Best Practices
Learn to test for API vulnerabilities and explore OWASP guidelines in this practical tutorial on identifying and addressing web API security issues.
Deploying and Upgrading Your First API in 30 Minutes or Less
Deploy and manage APIs efficiently using IBM API Connect. Learn to develop, secure, and upgrade APIs in a single environment, streamlining the process for beginners and experienced developers alike.
How to Steal ChatGPT's Embedding Size and Other Low-rank Logit Tricks
Uncover hidden information about API-protected LLMs through low-rank logit analysis. Learn to estimate embedding sizes, audit model updates, and identify source models efficiently.
Getting API Security Right
Explore best practices for securing APIs through real-world cases. Learn about attack surfaces, authorization issues, and actionable guidelines to enhance API security.
Google Family Link Field Test
Explore security vulnerabilities in Google Family Link and learn how teenagers can bypass restrictions using third-party apps. Discover mitigations to preserve digital wellbeing policies.

Common API Security Pitfalls
Explore common API security pitfalls, their root causes, and best practices for protection. Learn to assess and improve API security, ensuring robust defense against unauthorized access and data breaches.
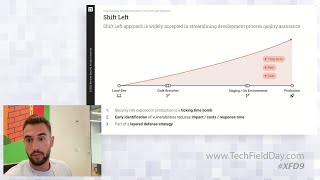
API Security Testing with Noname Security - Overview and Live Demo
Discover how to integrate API security testing into CI/CD pipelines with pre-production capabilities, ensuring rapid and secure API development through hands-on demonstrations.
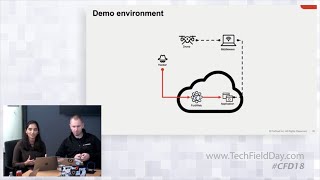
Leveraging Fortinet FortiWeb and FortiSOAR for Enhanced Cybersecurity
Discover how FortiWeb and FortiSOAR integrate to provide robust cybersecurity through API discovery, machine learning, and cloud technology, demonstrated via real-world scenarios including drone-based attacks.
Breaking Microsoft Teams and SharePoint Through Migration APIs
Uncover critical security vulnerabilities in Microsoft SharePoint Online's migration APIs and learn how threat actors can exploit these features to compromise Microsoft 365 services and Azure Active Directory.
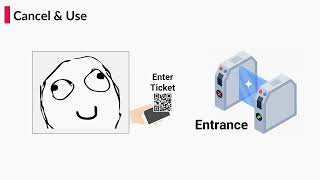
Vulnerabilities in Global Transportation Payment Systems - Security Risks and Exploits
Uncover critical security vulnerabilities in public transportation payment systems, focusing on Moovit's API weaknesses, unauthorized access risks, and solutions for protecting user data and preventing payment fraud.
BOLABuster - Harnessing LLMs for Automating BOLA Detection
Discover how to leverage LLMs for automated BOLA vulnerability detection in APIs and web applications, exploring BOLABuster's innovative approach to identifying critical security risks at scale.
Practical Exploitation of DoS in Bug Bounty Programs
Discover practical techniques for identifying and exploiting DoS vulnerabilities in bug bounty programs, covering N+1 errors, GraphQL crashing, and Cache Poisoning with real-world examples and responsible reporting practices.
Shield Your Backend from Outside Attacks with API Managers
Discover how to protect backend systems using API Managers, implement security layers, and defend against vulnerabilities while centralizing security configurations for robust API protection.
The Power of API-First Practices in Fashion Tech
Explore API-First practices in fashion tech, from ideation to execution. Learn how Inditex built an ecosystem empowering developers to innovate and ship faster.