Pacu - Attack and Post-Exploitation in AWS
Explore AWS attack and post-exploitation techniques using Pacu, an open-source tool for penetration testing and security assessments in cloud environments.
Secure Your AWS Accounts Without Breaking the Bank
Learn cost-effective strategies to enhance AWS account security, covering essential practices and tools for robust protection without excessive spending.
Breaking Formation - From an Error Message to Internal AWS Infrastructure
Explore a critical AWS CloudFormation vulnerability, its impact on cloud security, and the disclosure process. Gain insights into cloud infrastructure vulnerabilities and future research directions.
Security Enhanced on Groups Automation - AKA SEGA
Automatización de gestión de grupos de seguridad en AWS para Mercado Libre: de trabajo manual a controles automáticos. Solución escalable para múltiples cuentas y desarrolladores, manteniendo control sobre cambios en reglas.
AWS Well-Architected Framework - Security Pillar
Guía de estrategias para diseñar sistemas seguros en la nube, abordando gestión de identidades, detección, protección de infraestructura, protección de datos y respuesta a incidentes en AWS.
Step by Step AWS Cloud Hacking
Explore real-life AWS cloud exploitation techniques, from zero access to full privilege escalation and internal network access via custom AWS Client VPN, using practical concepts and tools.
DIAL - Did I Just Alert Lambda?
Explore DIAL, a stateless monitoring system for AWS that provides visibility on internal threats and security misconfigurations across multiple accounts, leveraging Lambda for scalability and easy deployment.
Distributed Commit Log - Application Techniques for Transaction Processing
Explore techniques for leveraging distributed commit logs in transaction processing, including handling duplicates, sharding, exceptions, and debugging in real-time systems.
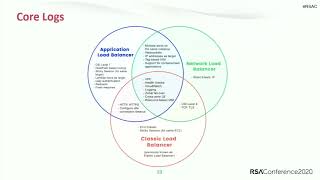
Logging in the Cloud - From Zero to Incident Response Hero
Learn essential cloud logging practices for AWS, Azure, and GCP to enhance incident response capabilities and streamline security operations in multi-cloud environments.
Strangeways, Here We Come
Explore cloud migration for startups: benefits, risks, and security best practices. Learn about AWS, cloud architecture, and strategies for a successful transition from on-premises to cloud-based solutions.
Managing Secrets in Your Cloud Environment - AWS, GCP, and Containers (and Beyond)
Comprehensive guide to managing sensitive data in cloud environments, covering storage options, common mistakes, identity considerations, evaluation criteria, and solutions for AWS, GCP, and Azure containers.
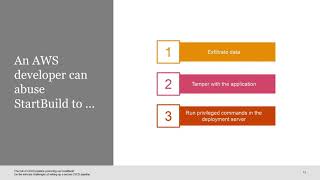
The Risk of CI - CD Pipeline Poisoning via CodeBuild
Explore CI/CD pipeline vulnerabilities in AWS services, focusing on CodeBuild abuse. Learn how small decisions can compromise security, bypass controls, and potentially lead to pipeline poisoning.
Deterministic Storage Performance - The AWS Way for Capacity Based QoS with OpenStack and Ceph
Explore deterministic storage performance in OpenStack and Ceph, emulating AWS EBS. Learn to manage QoS, combine Ceph pools with Cinder Volume Types, and optimize performance based on storage media.
Serverless Infections - Malware Just Found a New Home
Explore serverless architecture vulnerabilities and learn how malware can exploit AWS Lambda functions, with insights on prevention and security best practices.
Pentesting Swift Application with OWASP iGoat
Learn iOS Swift app pentesting using OWASP iGoat, covering security loopholes, defense strategies, and real-world case studies. Gain skills for product security engineers and bug bounty hunters.
All Your Cloud Are Belong To Us - Hunting Compromise in Azure
Explore techniques for identifying and mitigating compromises in Azure cloud environments, focusing on network security, threat detection, and best practices for cloud security.
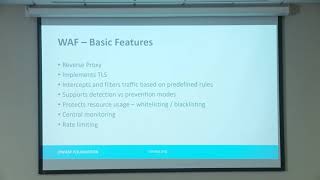
Your Frontier Defense - Understanding Web Application Firewalls
Explore WAF options, features, and challenges across cloud providers and self-managed solutions for enhanced web application security and defense-in-depth strategies.
Cloud Forensics - Putting The Bits Back Together
Explore cloud forensics challenges and solutions in AWS, focusing on server breaches, disk imaging, and incident response techniques for various EC2 instance types and EBS volumes.
Attacking Modern Web Technologies
Explore modern web vulnerabilities with top hacker Frans Rosén. Learn about exploiting postMessage, WebSockets, cloud misconfigurations, and more. Gain insights to enhance your web security knowledge.
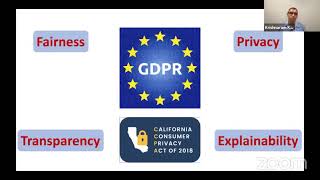
Responsible AI in Industry - Lessons Learned in Practice
Explore practical lessons on implementing responsible AI in industry, covering explainability, fairness, and challenges faced by major tech companies.
Sharding Containers - Make Go Apps Computer-Friendly Again
Explore automatic local sharding with Docker to optimize Go apps for high-throughput and high-load scenarios, improving performance and resource utilization.