Security Risks of Low-Code/No-Code Applications - What Could Go Wrong?
Explores security risks of low-code/no-code platforms used by business professionals. Presents research findings, demonstrates common security issues, and introduces OWASP framework for mitigating risks in business-led development.
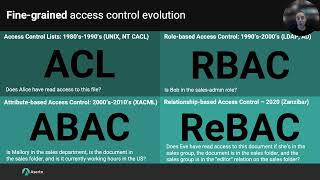
Cloud-Native Authorization Standards
Explore cloud-native authorization standards and their implementation in modern distributed systems for enhanced security and access control.
Integrity Protection and Access Control - Who Do You Trust?
Explore integrity protection and access control in Linux systems, focusing on mitigating physical attacks and enhancing security through hardware-backed encryption and specialized LSM implementations.
A Practical Approach to Applying Access Controls
Learn practical techniques for implementing effective access controls in cybersecurity systems, enhancing your ability to protect sensitive information and manage user permissions.
Permissions - Android Fundamentals
Learn essential Android permissions concepts, including implementation, handling, and best practices for secure app development.
Why Security Fails and How to Solve It - Lessons from Real-World Assessments
Explore real-world security failures and innovative solutions with insights from Praetorian's field experiences. Learn actionable steps to enhance cybersecurity through smarter practices and cutting-edge tools.
TOTPs Are Not As Secure As You Might Believe
Explore vulnerabilities in Time-based One-Time Passwords (TOTPs) and learn strategies to enhance their security in authentication systems.
Advanced API Security with Kong - Developer Day 2021 Labs
Learn to secure APIs using Kong Gateway and Okta. Configure OIDC authentication for Kong Developer Portal and Manager, and explore various security plugins and features.
AWS and Okta: New Best Practices for Identity Management and Security - One Year Later
Explore the latest AWS-Okta integration strategies, focusing on improved identity management, security practices, and operational efficiency for your AWS environments.
Making Permissions Accessible to Anyone With Permit.io
Explore challenges and best practices in permissions and access control with Or Weis from Permit.io, discussing solutions for making authorization accessible and efficient for developers.
Common Authorization Vulnerabilities and Best Practices
Explore common authorization vulnerabilities and best practices with Marco from Teleport. Learn about privilege management, multi-service security, and implementing effective authorization strategies.
Breaking Up With Network Policies - Developers Deserve Better
Exploring intent-based access control as an alternative to network policies, focusing on service-to-service security and zero trust approaches for better developer experience.
The Abridged History of Application Security
Explore the evolution of application security from the 1960s to present, highlighting improvements and inspiring security professionals with a historical perspective on industry progress.
The Secret Life of Secrets - Designing Secure API Keys
Explore API key design strategies, security measures, and best practices for creating robust and secure API authentication systems.
Collaborative and Private Data Processing with TEE-enforced Sticky Policy - Tech Talk
Explore TEE-enforced sticky policies for collaborative and private data processing in this insightful tech talk by Zhiqiang Lin.
Paved Roads to Express RBAC in Threat Models
Learn effective techniques for incorporating Role-Based Access Control (RBAC) into threat modeling, enhancing security design and risk assessment for software systems.
Network File System Security - Exploiting Misconceptions and Vulnerabilities
Explore Network File System security misconceptions and exploitation techniques. Gain insights into NFS protocol vulnerabilities and learn how to address common security pitfalls in enterprise environments.
A New Architecture for Data Security to Free Incident Responders from False Positives
Explore a new data security architecture that minimizes false positives, enhancing incident response efficiency and improving detection of real security threats.
IAM Confused - Getting Work Done and Keeping SecOps Happy
Explore effective IAM strategies to balance productivity and security in cloud environments, addressing common challenges and implementing best practices for access management.
PLSE Seminar Series - J. Aldrich "Using Capability-Based Modules to Enforce Secure Resource Usage"
Explores capability-based modules for secure resource management in programming languages, highlighting their benefits and applications in enhancing software security and reasoning.
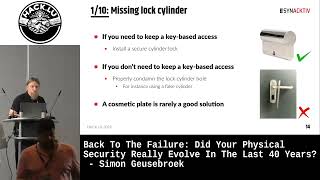
Back to the Failure - Did Your Physical Security Evolve in the Last 40 Years?
Explore the evolution of physical security over four decades, examining vulnerabilities, advancements, and critical lessons learned to strengthen modern security systems.