O-RAN Security Controls: Implementing Protection Measures for Open Radio Access Networks
Explore essential security controls and protective measures for O-RAN networks, from access control and encryption to intrusion detection and network segmentation strategies.
Understanding Zero Trust Architecture - Principles and Implementation
Explore the transformative principles of Zero Trust security, from "never trust, always verify" mindset to practical implementation strategies for enhanced network protection.
Secure Access for Your Workforce with Microsoft Entra Suite
Discover how unifying Conditional Access across identities and networks simplifies Zero Trust architecture while streamlining employee onboarding and securing remote access to applications and resources.
Zero Trust and the Identity Imperative - Building Resilience Against Emerging Threats
Discover how to strengthen Zero Trust security through identity management, following NIST guidelines while addressing modern threats like phishing and shadow IT to improve organizational resilience.
Detection is Not Enough - The Case for Zero Trust Controls for Better Endpoint Security
Discover essential zero trust control strategies and best practices for strengthening endpoint security in cloud environments through proven management techniques.
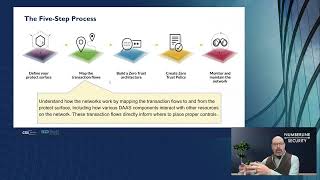
Applying the Five-Step Zero Trust Process and Why It Matters
Discover how to implement Zero Trust security using the Five-Step Process alongside CISA's maturity model, with practical examples and industry applications.
International Adoption of Zero Trust Security Strategy - Global Implementation and Challenges
Explore global Zero Trust security adoption trends, challenges, and best practices across regions and industries while learning key implementation strategies for enhanced cybersecurity.
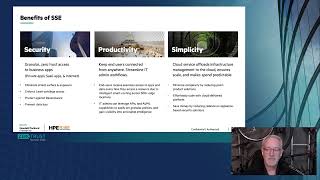
Transforming Security: The Power of Security Service Edge for Zero Trust Access
Discover how Security Service Edge (SSE) strengthens Zero Trust architecture, enhances network protection, and revolutionizes organizational security through modern implementation strategies.
Dynamic Defense - Context-Based Access Control and Zero Trust
Explore modern access control through zero trust principles, context-based security, and AI-driven threat detection for enhanced cybersecurity implementation and risk management.
Zero Trust Guidance for Critical Infrastructure
Gain insights into implementing Zero Trust security frameworks for critical infrastructure through expert guidance on modern protection strategies and implementation approaches.
Building Resilient Environments - Incorporating Security and Compliance into Database Monitoring
Discover essential strategies for database security and compliance monitoring, from vulnerability detection to access control implementation and audit processes for maintaining industry standards.
Enhancing Security with Istio - Realtime JWT Access Revocation
Discover how to implement real-time JWT token revocation in Istio systems through an event-based architecture, enabling enhanced security controls and immediate access management across multiple clusters.

Securing Outgoing Traffic: Building a Powerful Internet Egress Gateway for Reliable Connectivity
Master the implementation of secure Internet Egress gateways using Istio and Envoy, focusing on fine-grained access policies, multi-tenant architecture, and robust traffic monitoring for enhanced network security.
Your Cheat Code for API Authorization - From OpenAPI to Fine-Grained Access Control
Discover how to implement fine-grained API authorization using Topaz, an open-source service compatible with Open Policy Agent and Google Zanzibar ReBAC model, to manage complex microservices security effectively.
Reinventing Seccomp with eBPF and KRSI for Enhanced Kernel Security
Explore how eBPF and KRSI can enhance Linux kernel security beyond traditional Seccomp capabilities, with practical demonstrations for implementing advanced syscall filtering in containerized environments.
Building Multi-tenant Applications with Vercel and Auth0
Learn how to implement multi-tenant authentication in B2B applications using Auth0's sample app and deploy seamlessly with Vercel's integration for secure, scalable user management.

Shadow AI - The Dark Horse of Cybersecurity Threats
Discover how Shadow AI poses hidden cybersecurity risks, learn identification techniques, and implement strategies to protect organizational data and AI models from emerging threats.
Open Policy Agent (OPA) Introduction and Deep Dive with V1.0 Update
Dive into Open Policy Agent (OPA), exploring policy decision-making across cloud native stacks, from application authorization to Kubernetes admission, with insights into v1.0 features and updates.

Securing Outgoing Traffic: Building a Powerful Internet Egress Gateway for Reliable Connectivity
Master the implementation of secure Internet Egress gateways using Istio and Envoy, focusing on fine-grained access policies, multi-tenant capabilities, and robust traffic monitoring for enhanced network security.
GitHub for Fun, Profit, and Security
Master GitHub's advanced features for enhanced productivity, security, and efficient organization management through configuration-as-code solutions and best practices for access control.

Open Policy Agent (OPA) Introduction and Deep Dive with V1.0 Updates
Dive into policy decision-making with Open Policy Agent (OPA), exploring its role in cloud-native environments from application authorization to Kubernetes admission control and recent v1.0 updates.