FabAccess
Diskussion über FabAccess: Eine föderierbare Automatisierungsinfrastruktur für partizipative Communities wie Offene Werkstätten, die eine selbstgesteuerte, sichere und gleichberechtigte Nutzung von Ressourcen ermöglicht.
Practical Use of the MUD Specification to Support Access Control in the IoT
Explore how the MUD Specification can enhance IoT device access control through proof of concept implementations, addressing lessons learned and implementation challenges.
Lessons Learned Implementing Meaningful Access Controls to Customer Data
Insights on implementing robust access controls for customer data, reducing internal access by 70% through improved tooling, processes, and automation at Intercom.
Access Control with Concierge - One Tool to Rule Them All
Discover Concierge, a comprehensive solution for managing access to multiple SaaS services and internal tools, streamlining onboarding, offboarding, and role changes for IT operations teams.
Red Hat CloudForms - Turbocharge Your OpenStack
Enhance OpenStack with CloudForms for improved operations, monitoring, self-service, access control, and infrastructure management. Integrate with Ansible for automation and leverage policy engine for compliance and chargeback.
Supply Chain Unchained - How To Be A Bad SaaS
Explore software supply chain vulnerabilities, focusing on SaaS security. Learn about access control, API restrictions, maturity evaluation, logging, cloud security, and code integrity.
To Log, or Not to Log! That Is the Question - DefCamp - 2022
Explore logging challenges in cybersecurity, including sensitive data handling, storage, analysis, and access control. Learn best practices for secure logging in various scenarios.
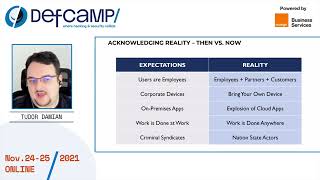
Demystifying Zero Trust - DefCamp - 2021
Explore Zero Trust security: its principles, implementation, and impact on cybersecurity. Learn about identity governance, least privilege, and maturity models for effective protection against modern threats.
Granular Trust - Making It Work
Explore granular trust models for enhanced security, covering authentication, access levels, and emergency protocols. Learn to implement flexible, context-aware security systems.
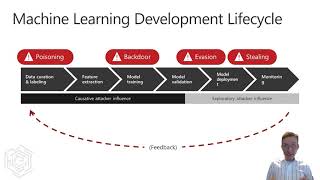
The Practical Divide between Adversarial ML Research and Security Practice - A Red Team Perspective
Exploring the gap between adversarial ML research and real-world security practices, highlighting challenges and lessons learned from Microsoft's Machine Learning Red Team engagement.
BeyondProd- The Origin of Cloud-Native Security at Google - Brandon Baker - USENIX Enigma - 2020
Exploring Google's BeyondProd: A cloud-native security model emphasizing service trust, workload isolation, and automated vulnerability management for microservices-based architectures.
Hacking Health - Security in Healthcare IT Systems - USENIX Enigma 2016
Explore healthcare IT security challenges, from doctor complexes to patient data access, and learn about vulnerabilities in medical devices, cloud systems, and wearable technology.
A Physical Security Plan for Implementing ISO 27002
Explore physical security implementation for ISO 27002, covering human resources, asset management, and access control. Learn from real-world examples and gain insights on testing, remediation, and continuous improvement.
OWASP Top 10 Proactive Controls
Comprehensive guide to OWASP Top 10 Proactive Controls for secure software development, covering essential techniques from query parameterization to threat modeling, presented by expert Jim Manico.
The Anatomy of a Secure Web Application in Java Using Spring Security and Apache Fortress
Practical guidance on implementing secure Java web applications using Spring Security and Apache Fortress. Covers authentication, authorization, and confidentiality controls with hands-on demos and code examples.
Attribute Based Access Control - Why, What, How
Explore digital identity trends, ABAC implementation, and data protection in finance. Learn from ABNAMRO's experience with Attribute Based Access Control and its impact on security and regulation compliance.
Controlled Mayhem With Cloud Native Security Pipelines
Explore cloud-native security pipelines, comparing traditional and modern approaches, while addressing challenges in container orchestration, access control, and CI/CD processes.
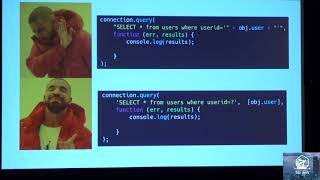
OWASP Top 10 for JavaScript Developers
Explore JavaScript vulnerabilities in OWASP Top 10, covering client and server-side issues with focus on modern frameworks and NodeJS. Learn prevention techniques for secure web development.
Testing and Hacking APIs
Learn techniques for testing and exploiting API vulnerabilities, including understanding implementation, detecting weak points, and conducting effective penetration tests on modern applications.

How to Write a Linux Security Module
Comprehensive guide to creating Linux Security Modules, covering infrastructure, interfaces, and best practices for implementing additional kernel security mechanisms.
Kubernetes for the Hybrid Enterprise
Explore Azure's Kubernetes solutions for hybrid enterprises, covering architecture, modernization, management, deployment, governance, and monitoring in distributed environments.