Overview and Recent Developments in TPM - Kernel Space Updates
Explore TPM subsystem updates, recent developments, and security measures against hardware attacks in Linux kernel space with Intel engineer Jarkko Sakkinen.
Insecurity Protocols - An Overview of Modern Authentication
Explore modern authentication protocols like OpenID Connect, SAML, and WebAuthn. Learn their strengths, vulnerabilities, and real-world security implications in this comprehensive overview.
Bypassing Entra ID Conditional Access - A Deep Dive Into Device Authentication Mechanisms
Explore device authentication in Entra ID, uncovering vulnerabilities in Conditional Access. Learn about attack methods, defense strategies, and gain insights into Microsoft's cloud security infrastructure.
How a Simple Misconfiguration Can Break TPM Full Disk Encryption
Explore TPM-based disk encryption vulnerabilities, learn to identify and exploit misconfigurations in Linux systems, and discover proper boot sequence validation techniques.
Extending Non-Repudiable Logs with eBPF
Explore how eBPF enhances TPM-based non-repudiable logging, enabling granular system integrity verification and container attestation for improved security and trust in Linux systems.
Updating Linux with TUX: Trust Update for Linux Kernel
Explore TUX, a system for maintaining Linux kernel integrity during updates. Learn about secure boot, TPM, and remote attestation to enhance platform trust and mitigate security threats.
Abusing Linux as a Trusted Bootloader
Explore Petitboot, a Linux-based bootloader for OpenPOWER firmware, and learn how it can be transformed into a trusted boot system using the linux-integrity subsystem and minimal kernel modifications.
Systemd and TPMs: Updates on Disk Encryption, PCR Policy Management, and More
Explore systemd's latest TPM-related features, including disk encryption, PCR policy management, measurement APIs, and event logging.
Fort Kairos - A New Dawn for Secure Linux in Untrusted Environments
Explore Fort Kairos, an open-source project revolutionizing secure Linux for untrusted edge environments using Trusted Boot, TPM, and disk encryption.

Securing Firmware - Secure and Trusted Boot in OpenBMC
Explore secure and trusted boot in OpenBMC, covering hardware root of trust, TPMs, keys, and signing while preserving user freedom to replace firmware securely.
Where Are Your Images Running? Stop Worrying and Start Encrypting!
Explore container image encryption for geofencing execution, ensuring trusted nodes run trusted images. Learn about DevOps, trust bootstrapping, and key management for secure container deployment.

Cisco Secure Connect - Zero Trust Network Architecture and SSE Integration
Discover how Cisco's Zero Trust Network Architecture integrates with SASE, featuring secure client implementation, MASQUE protocol adoption, and cross-platform support for enhanced network security and access control.
Recovery from Firmware Vulnerabilities in TPM - Securing Hardware Roots of Trust
Discover how new TPM specification APIs enable firmware vulnerability recovery and self-attestation capabilities, enhancing hardware security and trust restoration mechanisms.
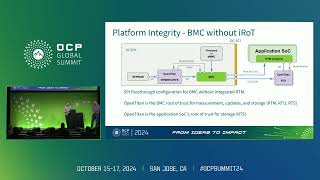
OpenTitan: Open-Source Hardware Root of Trust - Project Update
Discover the latest developments in OpenTitan's open-source hardware root of trust, including its architecture, security features, and applications for firmware protection and secret storage.
TPMs and the Linux Kernel - A Better Path to Hardware Security
Explore TPM integration with Linux kernel subsystems, focusing on practical approaches to hardware-based security implementation and simplified application-level access to TPM functionality.
TPM Security Enhancements to the Linux Kernel
Explore Linux kernel's latest TPM security enhancements, including attack defenses, secure communication protocols, and real-time monitoring capabilities for system protection.