BadXNU - Exploiting Vulnerabilities in Apple's XNU Kernel
Explore vulnerabilities in Apple's XNU kernel, uncovering security flaws and potential exploits in iOS and macOS systems.
Machswap - Stephen Parkinson
Explore iOS jailbreaking through machswap vulnerability, gaining insights into kernel access techniques and the iOS 12 jailbreak development process.
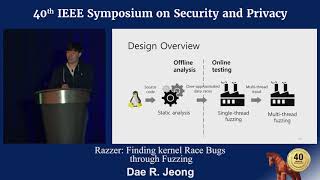
Razzer - Finding Kernel Race Bugs through Fuzzing
Discover efficient kernel race bug detection through fuzzing with Razzer. Learn static analysis and deterministic thread interleaving techniques to identify vulnerabilities in Linux kernels.
Android: Protecting the Kernel - Kernel Security Strategies
Explore Android kernel security, attack vectors, and defense strategies. Learn about SELinux, DAC capabilities, and new protections implemented in AOSP/Android-N to safeguard against rooting exploits.
Hypervisor-Enforced Kernel Integrity for Linux with KVM
Explore hypervisor-enforced kernel integrity for Linux using KVM. Learn about advanced protection mechanisms against kernel vulnerabilities and their implementation through virtualization.
Syzbot and the Tale of Thousand Kernel Bugs
Explore Linux kernel bug detection tools and their impact on system security. Learn about syzbot, syzkaller, and sanitizers for improving kernel stability and reliability.
Monitoring Surveillance Vendors - A Deep Dive into In-the-Wild Android Full Chains in 2021
Explore in-the-wild Android exploits discovered by Google's TAG and Android Security teams, including deep dives into CVE-2021-0920 and novel kernel exploitation techniques for bypassing hardware mitigations.
Adaptive Android Kernel Live Patching
Adaptive Android kernel live patching framework for securing devices against vulnerabilities, enabling hotpatching without source code access and automatic adjustment to different models and versions.
Automating Exploit Generation for Arbitrary Types of Kernel Vulnerabilities
Explore automated exploit generation techniques for kernel vulnerabilities, reducing development time from thousands of hours to minutes and enhancing cybersecurity practices.
Dive Into Apple IO80211Family Vol. 2
Explore Apple's Wi-Fi kernel extensions, uncovering new vulnerabilities and attack surfaces in the ever-evolving landscape of iOS security. Gain insights into the ongoing cat-and-mouse game of bug fixes and emerging threats.
How to Find Bugs in USB Device Drivers
Explore USB device driver vulnerabilities using vUSBf framework. Learn about fuzzing techniques, bug detection, and potential security risks in USB implementations across various operating systems.
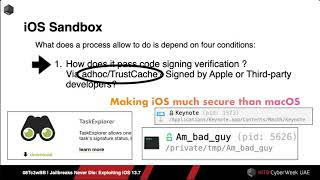
Jailbreaks Never Die - Exploiting iOS 13.7
Unveiling iOS 13.7 exploit chain: kernel vulnerabilities, mitigation bypasses, and techniques for reading/writing kernel memory. Insights into iOS security research and jailbreak development.
Escaping Virtualized Containers
Explore container escape techniques and new sandboxing tools using unikernels, lightweight VMs, and userspace-kernels to enhance isolation between host and container OS.
Cautious - A New Exploitation Method! No Pipe but as Nasty as Dirty Pipe
Unveils a novel exploitation technique surpassing Dirty Pipe, enabling arbitrary file overwriting and privilege escalation through double-free vulnerabilities, applicable across affected kernel versions.

Black Hat USA 2025
Black Hat USA 2025

Black Hat Asia 2024
Black Hat Asia 2024

Black Hat Europe 2023
Black Hat Europe 2023

Black Hat Asia 2025
Black Hat Asia 2025

Black Hat Europe 2024
Black Hat Europe 2024