Demystifying LLMs and Their Security Implications - A Business-Friendly Overview
Explore GenAI and LLMs, understanding their operations, security implications, and deployment scenarios. Learn to manage risks, prevent data leakage, and implement practical strategies for safe AI integration.
Malice in Chains - Supply Chain Attacks Using Machine Learning Models
Explore potential supply chain vulnerabilities in machine learning models and learn strategies to mitigate risks in AI-driven systems.
Creating an AI Security and Incident Response Team
Learn to establish and operate an AI Security and Incident Response Team (AISIRT) to address AI/ML system issues, detect problems, and differentiate between various threats.
Guarding LLM and NLP APIs: A Trailblazing Odyssey for Enhanced Security - Podcast #190
Explore LLM and NLP API security challenges, threat modeling, and defense strategies. Gain insights on OWASP Top 10 for LLM Applications and the AI Village's 'Hack the Future' event at Defcon31.
OWASP Top 10 Security Risks for Large Language Models
Explore OWASP Top 10 LLM security risks, learn mitigation strategies, and understand the impact of Generative AI on cybersecurity in various industries.
Learning Under Data Poisoning
Explore data poisoning's impact on machine learning, its detection methods, and strategies for building robust models against adversarial attacks in this informative talk.
Trustworthy Machine Learning: Challenges and Frameworks
Exploring the security challenges in machine learning, this talk discusses strategies for building trustworthy AI systems by analyzing data influence, addressing vulnerabilities, and enhancing interpretability.
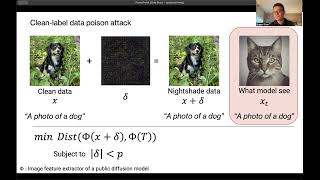
Nightshade: Prompt-Specific Poisoning Attacks on Text-to-Image Generative Models - Session 335
Explore poisoning attacks on text-to-image models, focusing on the Nightshade technique's ability to manipulate AI-generated images through targeted data manipulation.
Adversarial AI/ML Issues and Defense Strategies
Explore adversarial AI/ML challenges and defense mechanisms with Dr. Dipankar Dasgupta, gaining insights into critical cybersecurity strategies for machine learning systems.
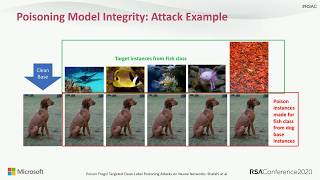
AI Security Engineering - Modeling - Detecting - Mitigating New Vulnerabilities
Explore AI security threats, including adversarial attacks and data poisoning. Learn detection, protection, and mitigation strategies for AI/ML systems from Microsoft experts.
Smashing the ML Stack for Fun and Lawsuits
Explore legal risks and ethical considerations of testing commercial ML systems' security, with insights on potential lawsuits and regulatory implications for researchers.
Poisoning Web-Scale Training Datasets is Practical
Explore strategies for creating large datasets and two attacks exploiting these mechanics, revealing vulnerabilities in deep learning models trained on internet-sourced data.
Breaking NBAD & UEBA Detection
Explore techniques to bypass Network Behavior Anomaly Detection (NBAD) and User Entity Behavior Analytics (UEBA), covering data poisoning, exfiltration, and various attack methods with live demonstrations.
Breaking NBAD and UEBA Detection
Explore techniques to bypass Network Behavior Anomaly Detection and User Entity Behavioral Analysis, including data poisoning, behavioral spoofing, and network manipulation strategies.
End-to-End Secure Machine Learning Development - Building a Secure AI Supply Chain
Discover essential security practices for AI development, from dataset handling to production deployment, focusing on supply chain security, model provenance, and risk mitigation in machine learning applications.
AI Safety, Security, and Play - Episode 137
Explore AI safety and security with David Haber, covering prompt injections, data poisoning, LLM vulnerabilities, and approaches to handling sensitive data in AI models.
OWASP Top 10 for Machine Learning Security - A Comprehensive Walkthrough
Explore OWASP's top 10 ML security vulnerabilities, gain insights into real-world examples, and learn actionable strategies for securing machine learning models and systems.
The Dark Side of AI: Hidden Supply Chain Risks in Open-Source AI Models
Explore security vulnerabilities in open-source AI models, including live demonstrations of exploits and techniques for embedding malicious code and data poisoning.
Safeguarding Machine Learning Systems - A Comprehensive Security Plan
Discover a holistic security framework for ML systems, covering data protection, model fortification, platform security, compliance measures, and human-centric safeguards for robust AI deployment.