STM32マイコン・セキュリティ - STM32H5でセキュア・マネージャをはじめよう
STM32H5マイコンの「STM32Trust TEEセキュア・マネージャ」を紹介。IoTセキュリティ強化に貢献する業界初の信頼できる実行環境の概念と評価方法を解説。
OP-TEE: Using TrustZone to Protect Our Own Secrets
Explore TrustZone technology for securing sensitive data in ARM CPUs, its potential applications, and the open-source OP-TEE implementation for Linux, with insights on current limitations and future possibilities.
TEEP Implementation on RISC-V Keystone and Arm TrustZone
Explore TEEP implementation on RISC-V Keystone and Arm TrustZone, covering use cases, prototypes, and CBOR expressions for secure execution environments.
TEEP Implementation on RISC-V Keystone and Arm TrustZone
Explore TEEP implementation on RISC-V Keystone and Arm TrustZone, focusing on secure provisioning techniques for trusted execution environments in embedded systems.
Systems & Networks Seminar - Andrew Bauman - Komodo: Using Verification to Disentangle Secure-Enclave Hardware from Software
Explores Komodo, an alternative to Intel SGX for secure enclaves, using verified software to implement isolated execution environments with improved flexibility and security guarantees.
Trusted Execution Environments - A Technical Overview of Intel SGX, Arm TrustZone, and RISC-V PMP
Explore key trusted execution environments: Intel SGX, Arm TrustZone, and RISC-V PMP. Learn their architectures, security features, and implementation processes for robust data protection.
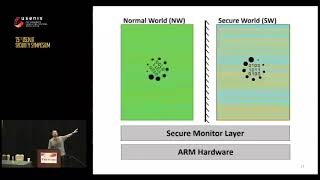
fTPM - A Software-Only Implementation of a TPM Chip
Explore software-based TPM implementation using ARM TrustZone, overcoming hardware limitations to provide robust security features for trusted computing in mobile devices.
Forging the USB Armory
Explore the development of an open-source USB-sized computer for security applications, featuring advanced SoC technology, secure boot, and ARM TrustZone implementation.
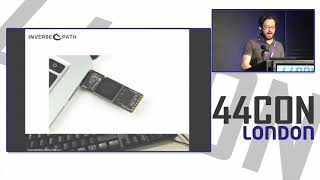
Forging the USB Armory
Explore the development of the USB armory, an open-source hardware device for security applications. Learn about its architecture, security features, and potential uses as a trusted USB device.
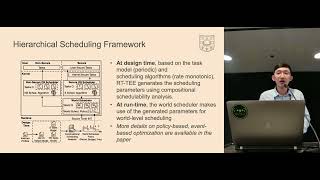
RT-TEE - Real-time System Availability for Cyber-physical Systems using ARM TrustZone
Explore real-time system availability for cyber-physical systems using ARM TrustZone technology, focusing on enhancing security and performance in critical applications.
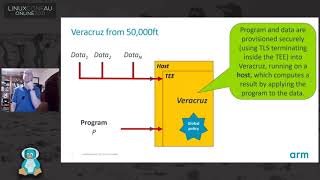
Veracruz - Privacy-Preserving Multiparty Computation Using Trusted Hardware
Explore privacy-preserving computation using secure enclaves, enabling secret data processing on untrusted hosts. Learn about Veracruz's implementation, security measures, and potential applications in multiparty scenarios.
Virtualizing Arm TrustZone on KVM
Extend KVM to virtualize Arm TrustZone, enabling VMs to run trusted execution environments. Explore implementation details, challenges, and future directions for secure virtualization.
OP-TEE is Ready - Let's Use It
Explore OP-TEE's capabilities and practical applications in secure embedded systems with expert guidance from Pengutronix e.K.'s Rouven Czerwinski.
Myth and Truth About Hypervisor-Based Kernel Protector - The Reason Why You Need Shadow-Box
Explore hypervisor-based kernel protection, its limitations, and the need for higher-privilege solutions like Shadow-Box to combat rootkits and kernel exploits effectively.